


Monolithic Terraform vs. Micro-State Architecture: Where Do You Draw the Blast Radius Line?
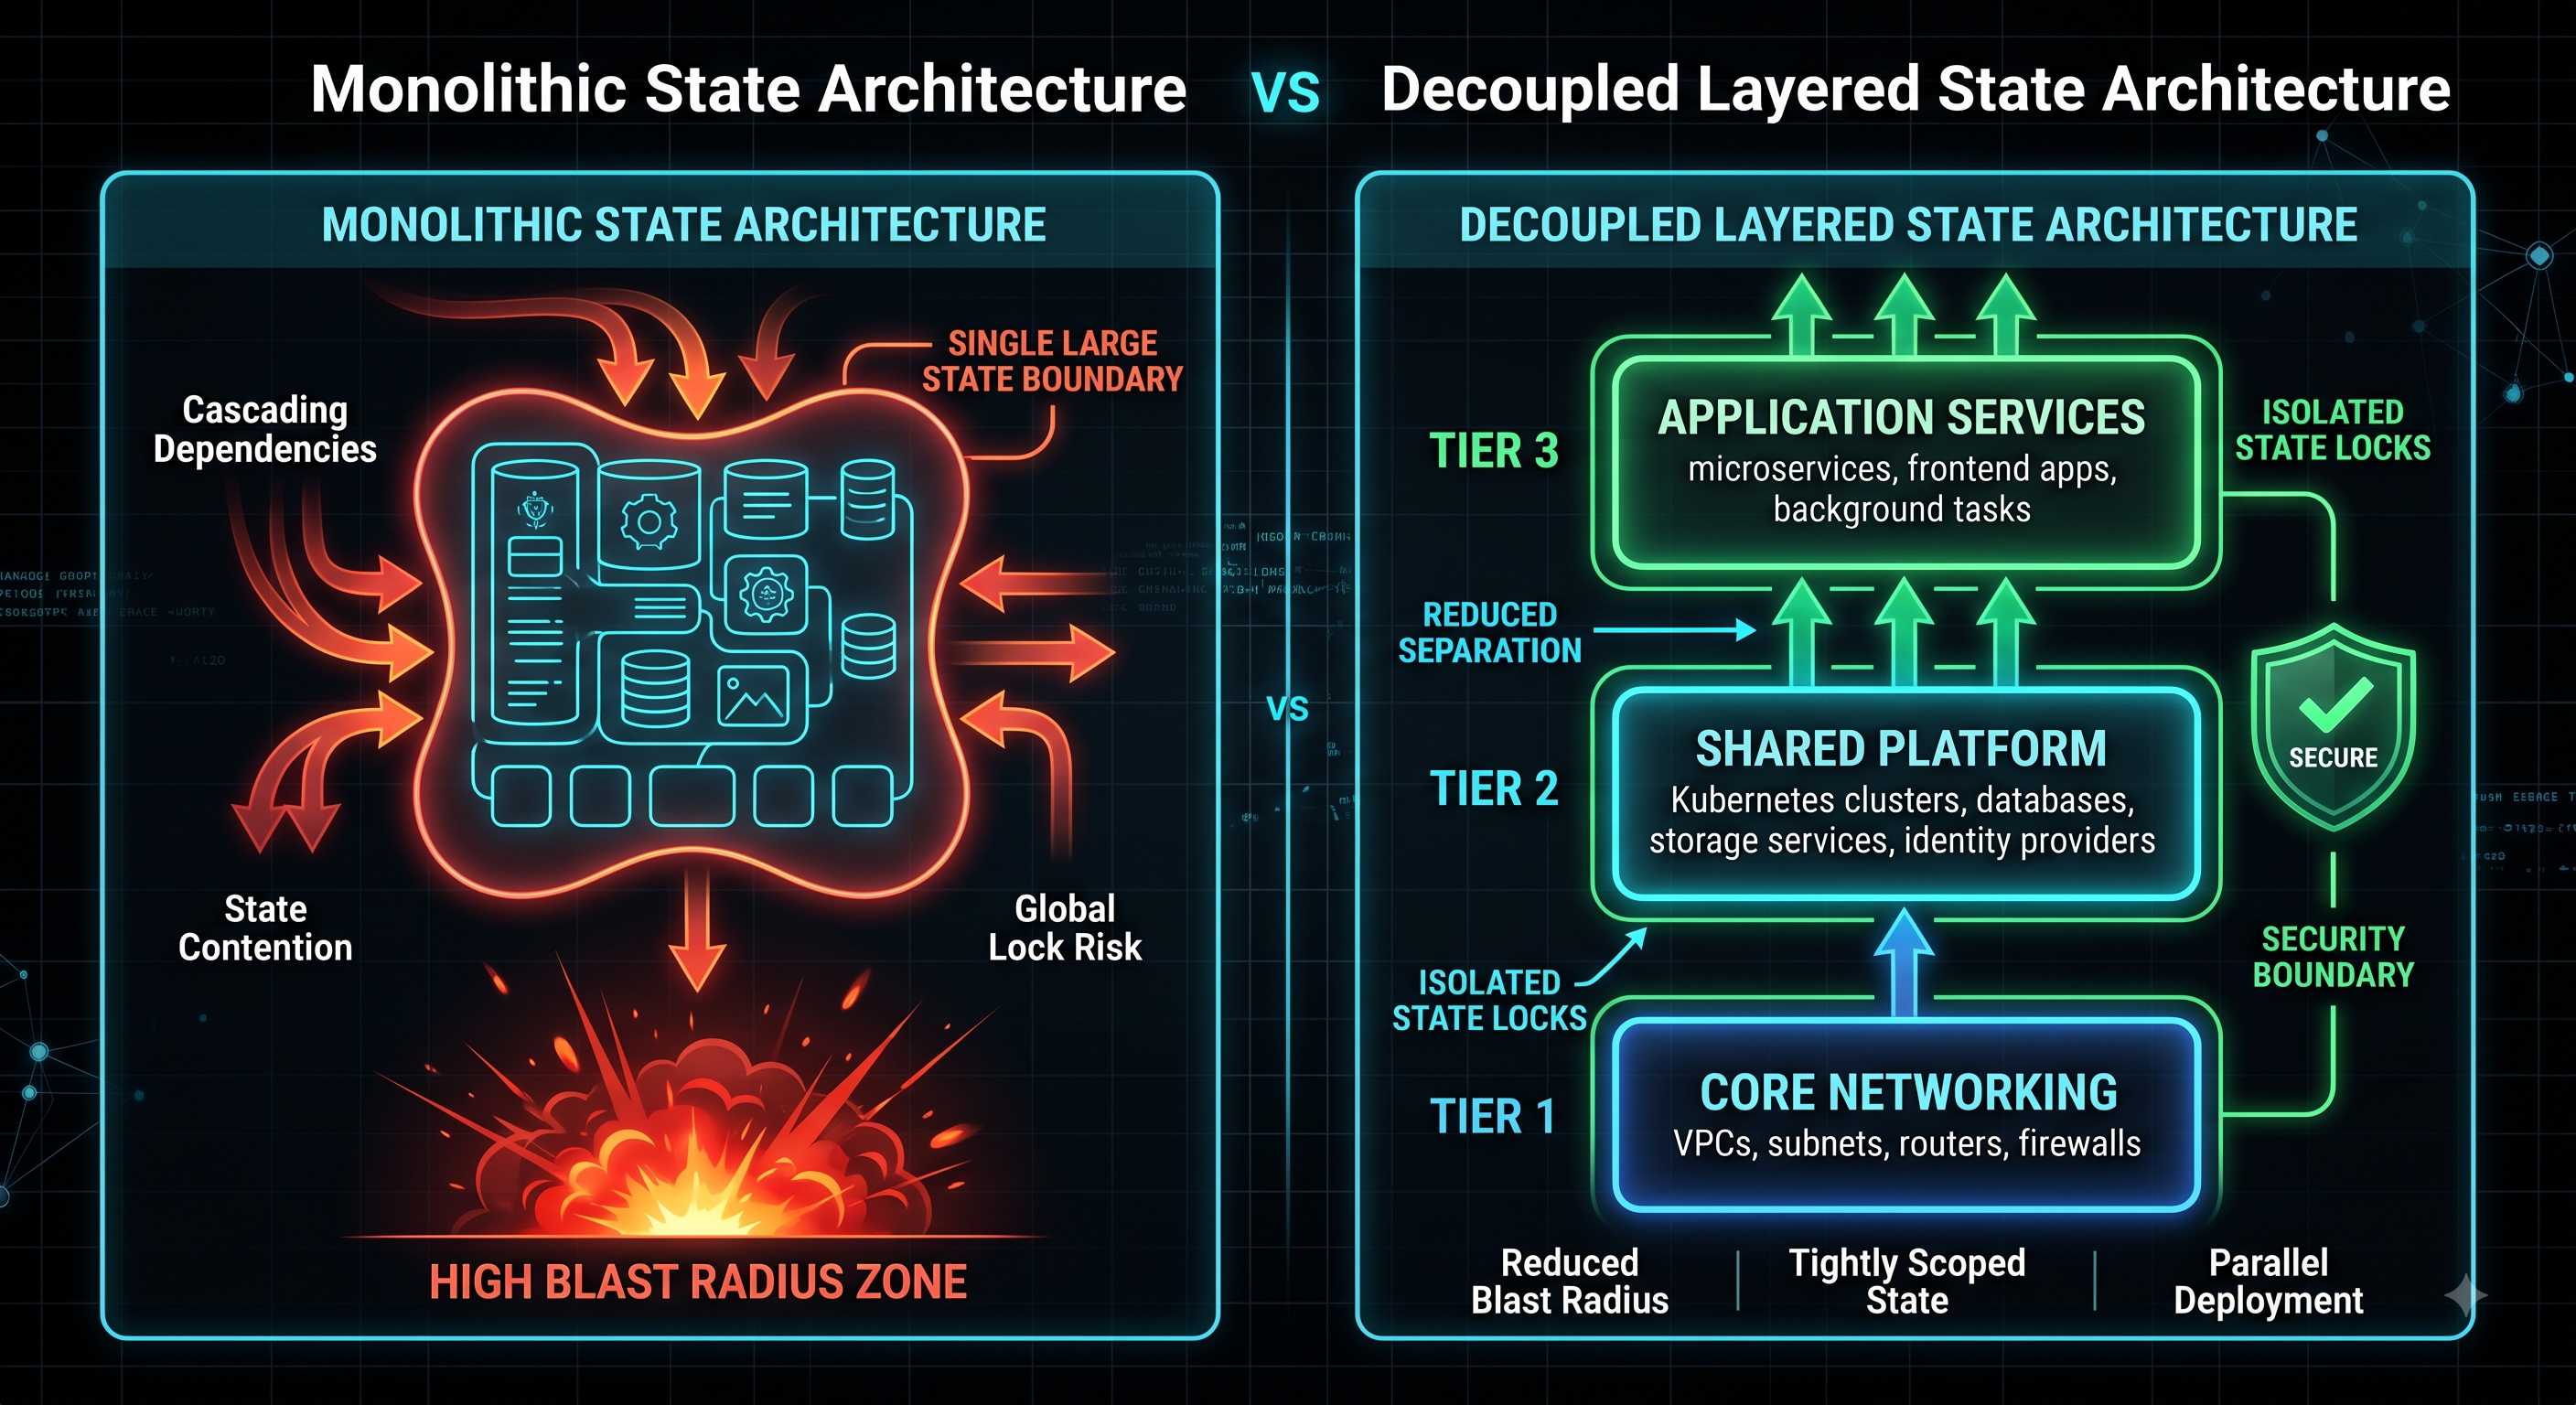
As infrastructure scales, Infrastructure as Code (IaC) architectures inevitably face a structural crossroads: do you keep environments grouped for easier reference, or decouple them into micro-states to minimize the blast radius?
A massive, centralized state file creates lock contention across teams, slows down execution plans to a crawl, and increases the risk of accidental drift. However, over-fragmenting state files introduces dependency sprawl, complex data-sharing layers via terraform_remote_state, and orchestration friction.
To balance safety and operational velocity, mature platform teams structure their IaC layers around stability and lifecycle frequency:
Layer 1: Foundational / Infrequent Changes (Low Blast Risk)
VPCs, subnets, transit gateways, and IAM base roles. These change rarely and should live in dedicated, tightly locked state files.
Layer 2: Core Platform & Data Services (Moderate Lifecycle)
Managed Kubernetes clusters, shared databases, and ingress gateways. Decoupled from application-level logic to prevent infrastructure rebuilds during app updates.
Layer 3: Ephemeral & Application Workloads (High Frequency)
Serverless functions, routing rules, deployment manifests, and autoscaling groups. Managed through autonomous states or application-scoped pipelines.
How does your engineering team manage this trade-off?
Do you break states down by environment, by lifecycle tier, or by domain-driven feature teams?
Key Takeaways
Monolithic state files drastically increase the blast radius of inadvertent configuration errors and pipeline locks.
Over-modularizing state files can lead to complex dependency management and orchestration overhead.
Separate state files based on resource volatility: foundational networking vs. rapidly changing application tiers.
Restrict write permissions to foundational state backends using automated CI/CD runners rather than local developer access.
CTA
Want to dive deep into cloud architecture patterns, GitOps workflows, and resilient DevOps infrastructure?
Join Techawks Cloud, DevOps & Open Source to collaborate with practicing cloud engineers, exchange IaC blueprints, and level up your platform engineering skills.
As infrastructure scales, Infrastructure as Code (IaC) architectures inevitably face a structural crossroads: do you keep environments grouped for easier reference, or decouple them into micro-states to minimize the blast radius?
A massive, centralized state file creates lock contention across teams, slows down execution plans to a crawl, and increases the risk of accidental drift. However, over-fragmenting state files introduces dependency sprawl, complex data-sharing layers via terraform_remote_state, and orchestration friction.
To balance safety and operational velocity, mature platform teams structure their IaC layers around stability and lifecycle frequency:
Layer 1: Foundational / Infrequent Changes (Low Blast Risk)
VPCs, subnets, transit gateways, and IAM base roles. These change rarely and should live in dedicated, tightly locked state files.
Layer 2: Core Platform & Data Services (Moderate Lifecycle)
Managed Kubernetes clusters, shared databases, and ingress gateways. Decoupled from application-level logic to prevent infrastructure rebuilds during app updates.
Layer 3: Ephemeral & Application Workloads (High Frequency)
Serverless functions, routing rules, deployment manifests, and autoscaling groups. Managed through autonomous states or application-scoped pipelines.
How does your engineering team manage this trade-off?
Do you break states down by environment, by lifecycle tier, or by domain-driven feature teams?
Key Takeaways
Monolithic state files drastically increase the blast radius of inadvertent configuration errors and pipeline locks.
Over-modularizing state files can lead to complex dependency management and orchestration overhead.
Separate state files based on resource volatility: foundational networking vs. rapidly changing application tiers.
Restrict write permissions to foundational state backends using automated CI/CD runners rather than local developer access.
CTA
Want to dive deep into cloud architecture patterns, GitOps workflows, and resilient DevOps infrastructure?
Join Techawks Cloud, DevOps & Open Source to collaborate with practicing cloud engineers, exchange IaC blueprints, and level up your platform engineering skills.
Monolithic Terraform vs. Micro-State Architecture: Where Do You Draw the Blast Radius Line?
As infrastructure scales, Infrastructure as Code (IaC) architectures inevitably face a structural crossroads: do you keep environments grouped for easier reference, or decouple them into micro-states to minimize the blast radius?
A massive, centralized state file creates lock contention across teams, slows down execution plans to a crawl, and increases the risk of accidental drift. However, over-fragmenting state files introduces dependency sprawl, complex data-sharing layers via terraform_remote_state, and orchestration friction.
To balance safety and operational velocity, mature platform teams structure their IaC layers around stability and lifecycle frequency:
Layer 1: Foundational / Infrequent Changes (Low Blast Risk)
VPCs, subnets, transit gateways, and IAM base roles. These change rarely and should live in dedicated, tightly locked state files.
Layer 2: Core Platform & Data Services (Moderate Lifecycle)
Managed Kubernetes clusters, shared databases, and ingress gateways. Decoupled from application-level logic to prevent infrastructure rebuilds during app updates.
Layer 3: Ephemeral & Application Workloads (High Frequency)
Serverless functions, routing rules, deployment manifests, and autoscaling groups. Managed through autonomous states or application-scoped pipelines.
How does your engineering team manage this trade-off?
Do you break states down by environment, by lifecycle tier, or by domain-driven feature teams?
Key Takeaways
Monolithic state files drastically increase the blast radius of inadvertent configuration errors and pipeline locks.
Over-modularizing state files can lead to complex dependency management and orchestration overhead.
Separate state files based on resource volatility: foundational networking vs. rapidly changing application tiers.
Restrict write permissions to foundational state backends using automated CI/CD runners rather than local developer access.
CTA
Want to dive deep into cloud architecture patterns, GitOps workflows, and resilient DevOps infrastructure?
Join Techawks Cloud, DevOps & Open Source to collaborate with practicing cloud engineers, exchange IaC blueprints, and level up your platform engineering skills.

 English
 Arabic
 French
 Spanish
 Portuguese
 Deutsch
 Turkish
 Dutch
 Italiano
 Russian
 Portuguese (Brazil)
 Greek