


Ofcom’s Online Safety Act Enforcement Wave: The UK Platform Architect’s Production Readiness Checklist
Ofcom’s regulatory supervision and enforcement roadmap is actively transitioning from consultation to direct technical accountability. For engineering teams building user-to-user (U2U) services, search functionality, or recommendation-driven platforms accessible in the UK, safety-by-design is now an infrastructure mandate rather than a policy guideline.
Why It Matters to UK Tech Teams
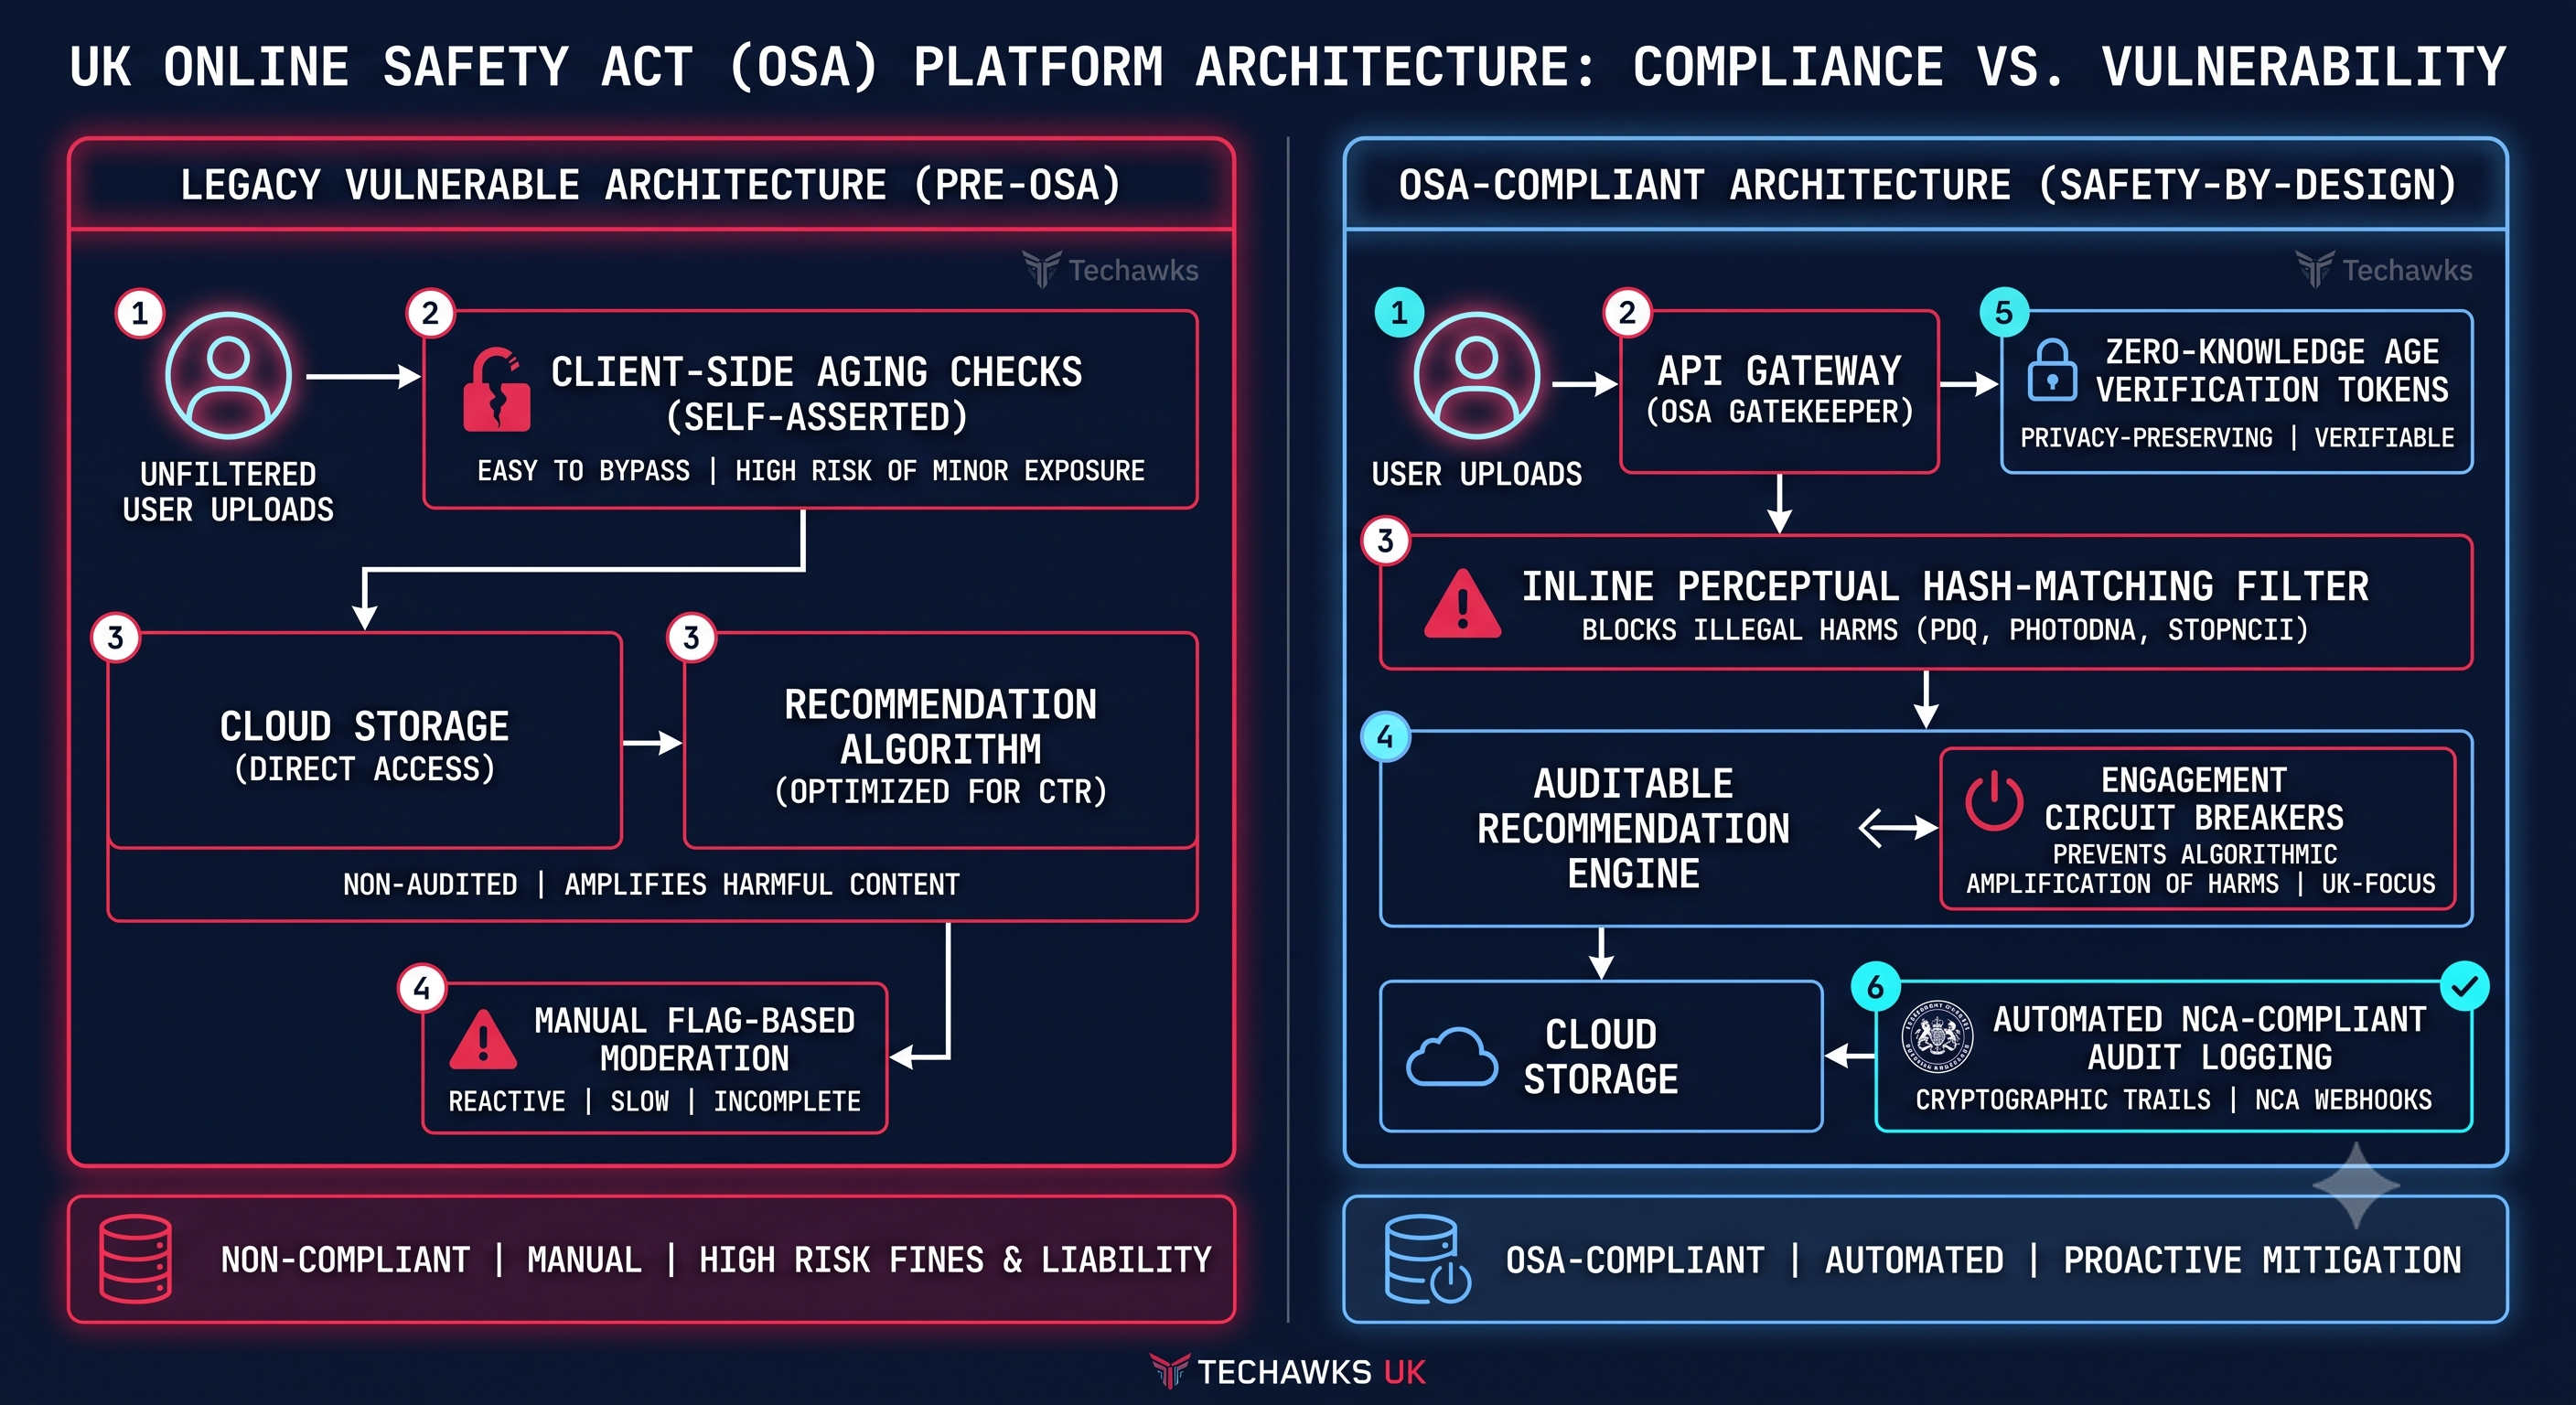
Ofcom has made it clear: platform moderation cannot remain a passive reporting workflow. Systems must demonstrate proactive risk mitigation, automated hash-matching against illegal harms, verifiable age-assurance gates, and auditable feed recommendation algorithms.
Non-compliance carries statutory penalties up to £18 million or 10% of qualifying worldwide revenue—along with potential personal liability for designated senior managers in severe obstruction cases.
The UK Platform Engineering Readiness Checklist
[ ] 1. Decouple Age Assurance from Permissive Client-Side Flags
└─ Replace self-declaration dropdowns with privacy-preserving age assurance (e.g., zero-knowledge attribute verification or tokenized estimation).
└─ Isolate adult-targeted schema pathways at the API gateway layer to prevent child profile exposure.
[ ] 2. Pipeline-Level Hash Matching for Priority Illegal Harms
└─ Integrate real-time media ingestion filters using cryptographic perceptual hashing (e.g., PDQ, PhotoDNA, StopNCII endpoints).
└─ Automate immediate quarantine queues prior to rendering payloads on public CDNs.
[ ] 3. Audit Recommender Systems for Amplification Vectors
└─ Instrument real-time circuit breakers that down-rank or unindex anomalous engagement spikes flagged for harmful or coordinated abuse.
└─ Expose user-facing feed customisation levers allowing adults to opt out of predictive algorithmic profiling.
[ ] 4. Build Automated Regulatory Escalation & Reporting Endpoints
└─ Establish direct NCA (National Crime Agency) webhook integration pipelines for validated priority illegal payloads.
└─ Ensure payload capture preserves non-tamperable cryptographic audit logs for Ofcom supervision requests.
[ ] 5. Mandate Third-Party SDK & User-Generated Data Audits
└─ Restrict unvetted third-party telemetry libraries tracking minors or indexing unmoderated comment components.
└─ Enforce end-to-end data minimisation across chat, messaging, and forum microservices.
Compliance under the OSA cannot be achieved with retroactive moderation—it requires building preventative boundaries into the ingestion and recommendation pipeline before bytes hit client devices.
Discussion Question
How is your infrastructure team balancing privacy-preserving zero-knowledge proofs with Ofcom's mandated age-assurance requirements across UK user sessions?
CTA (Join Techawks UK)
Follow Techawks UK for practical engineering architectures, regulatory compliance teardowns, and system design strategies built for the UK and European tech ecosystem.
Ofcom’s regulatory supervision and enforcement roadmap is actively transitioning from consultation to direct technical accountability. For engineering teams building user-to-user (U2U) services, search functionality, or recommendation-driven platforms accessible in the UK, safety-by-design is now an infrastructure mandate rather than a policy guideline.
Why It Matters to UK Tech Teams
Ofcom has made it clear: platform moderation cannot remain a passive reporting workflow. Systems must demonstrate proactive risk mitigation, automated hash-matching against illegal harms, verifiable age-assurance gates, and auditable feed recommendation algorithms.
Non-compliance carries statutory penalties up to £18 million or 10% of qualifying worldwide revenue—along with potential personal liability for designated senior managers in severe obstruction cases.
The UK Platform Engineering Readiness Checklist
[ ] 1. Decouple Age Assurance from Permissive Client-Side Flags
└─ Replace self-declaration dropdowns with privacy-preserving age assurance (e.g., zero-knowledge attribute verification or tokenized estimation).
└─ Isolate adult-targeted schema pathways at the API gateway layer to prevent child profile exposure.
[ ] 2. Pipeline-Level Hash Matching for Priority Illegal Harms
└─ Integrate real-time media ingestion filters using cryptographic perceptual hashing (e.g., PDQ, PhotoDNA, StopNCII endpoints).
└─ Automate immediate quarantine queues prior to rendering payloads on public CDNs.
[ ] 3. Audit Recommender Systems for Amplification Vectors
└─ Instrument real-time circuit breakers that down-rank or unindex anomalous engagement spikes flagged for harmful or coordinated abuse.
└─ Expose user-facing feed customisation levers allowing adults to opt out of predictive algorithmic profiling.
[ ] 4. Build Automated Regulatory Escalation & Reporting Endpoints
└─ Establish direct NCA (National Crime Agency) webhook integration pipelines for validated priority illegal payloads.
└─ Ensure payload capture preserves non-tamperable cryptographic audit logs for Ofcom supervision requests.
[ ] 5. Mandate Third-Party SDK & User-Generated Data Audits
└─ Restrict unvetted third-party telemetry libraries tracking minors or indexing unmoderated comment components.
└─ Enforce end-to-end data minimisation across chat, messaging, and forum microservices.
Compliance under the OSA cannot be achieved with retroactive moderation—it requires building preventative boundaries into the ingestion and recommendation pipeline before bytes hit client devices.
Discussion Question
How is your infrastructure team balancing privacy-preserving zero-knowledge proofs with Ofcom's mandated age-assurance requirements across UK user sessions?
CTA (Join Techawks UK)
Follow Techawks UK for practical engineering architectures, regulatory compliance teardowns, and system design strategies built for the UK and European tech ecosystem.
Ofcom’s Online Safety Act Enforcement Wave: The UK Platform Architect’s Production Readiness Checklist
Ofcom’s regulatory supervision and enforcement roadmap is actively transitioning from consultation to direct technical accountability. For engineering teams building user-to-user (U2U) services, search functionality, or recommendation-driven platforms accessible in the UK, safety-by-design is now an infrastructure mandate rather than a policy guideline.
Why It Matters to UK Tech Teams
Ofcom has made it clear: platform moderation cannot remain a passive reporting workflow. Systems must demonstrate proactive risk mitigation, automated hash-matching against illegal harms, verifiable age-assurance gates, and auditable feed recommendation algorithms.
Non-compliance carries statutory penalties up to £18 million or 10% of qualifying worldwide revenue—along with potential personal liability for designated senior managers in severe obstruction cases.
The UK Platform Engineering Readiness Checklist
[ ] 1. Decouple Age Assurance from Permissive Client-Side Flags
└─ Replace self-declaration dropdowns with privacy-preserving age assurance (e.g., zero-knowledge attribute verification or tokenized estimation).
└─ Isolate adult-targeted schema pathways at the API gateway layer to prevent child profile exposure.
[ ] 2. Pipeline-Level Hash Matching for Priority Illegal Harms
└─ Integrate real-time media ingestion filters using cryptographic perceptual hashing (e.g., PDQ, PhotoDNA, StopNCII endpoints).
└─ Automate immediate quarantine queues prior to rendering payloads on public CDNs.
[ ] 3. Audit Recommender Systems for Amplification Vectors
└─ Instrument real-time circuit breakers that down-rank or unindex anomalous engagement spikes flagged for harmful or coordinated abuse.
└─ Expose user-facing feed customisation levers allowing adults to opt out of predictive algorithmic profiling.
[ ] 4. Build Automated Regulatory Escalation & Reporting Endpoints
└─ Establish direct NCA (National Crime Agency) webhook integration pipelines for validated priority illegal payloads.
└─ Ensure payload capture preserves non-tamperable cryptographic audit logs for Ofcom supervision requests.
[ ] 5. Mandate Third-Party SDK & User-Generated Data Audits
└─ Restrict unvetted third-party telemetry libraries tracking minors or indexing unmoderated comment components.
└─ Enforce end-to-end data minimisation across chat, messaging, and forum microservices.
Compliance under the OSA cannot be achieved with retroactive moderation—it requires building preventative boundaries into the ingestion and recommendation pipeline before bytes hit client devices.
Discussion Question
How is your infrastructure team balancing privacy-preserving zero-knowledge proofs with Ofcom's mandated age-assurance requirements across UK user sessions?
CTA (Join Techawks UK)
Follow Techawks UK for practical engineering architectures, regulatory compliance teardowns, and system design strategies built for the UK and European tech ecosystem.

 English
 Arabic
 French
 Spanish
 Portuguese
 Deutsch
 Dutch
 Italiano
 Russian
 Romaian
 Portuguese (Brazil)
 Greek