


The Cyber Security & Resilience Bill: Is Your UK Tech Stack Actually Audit-Ready?
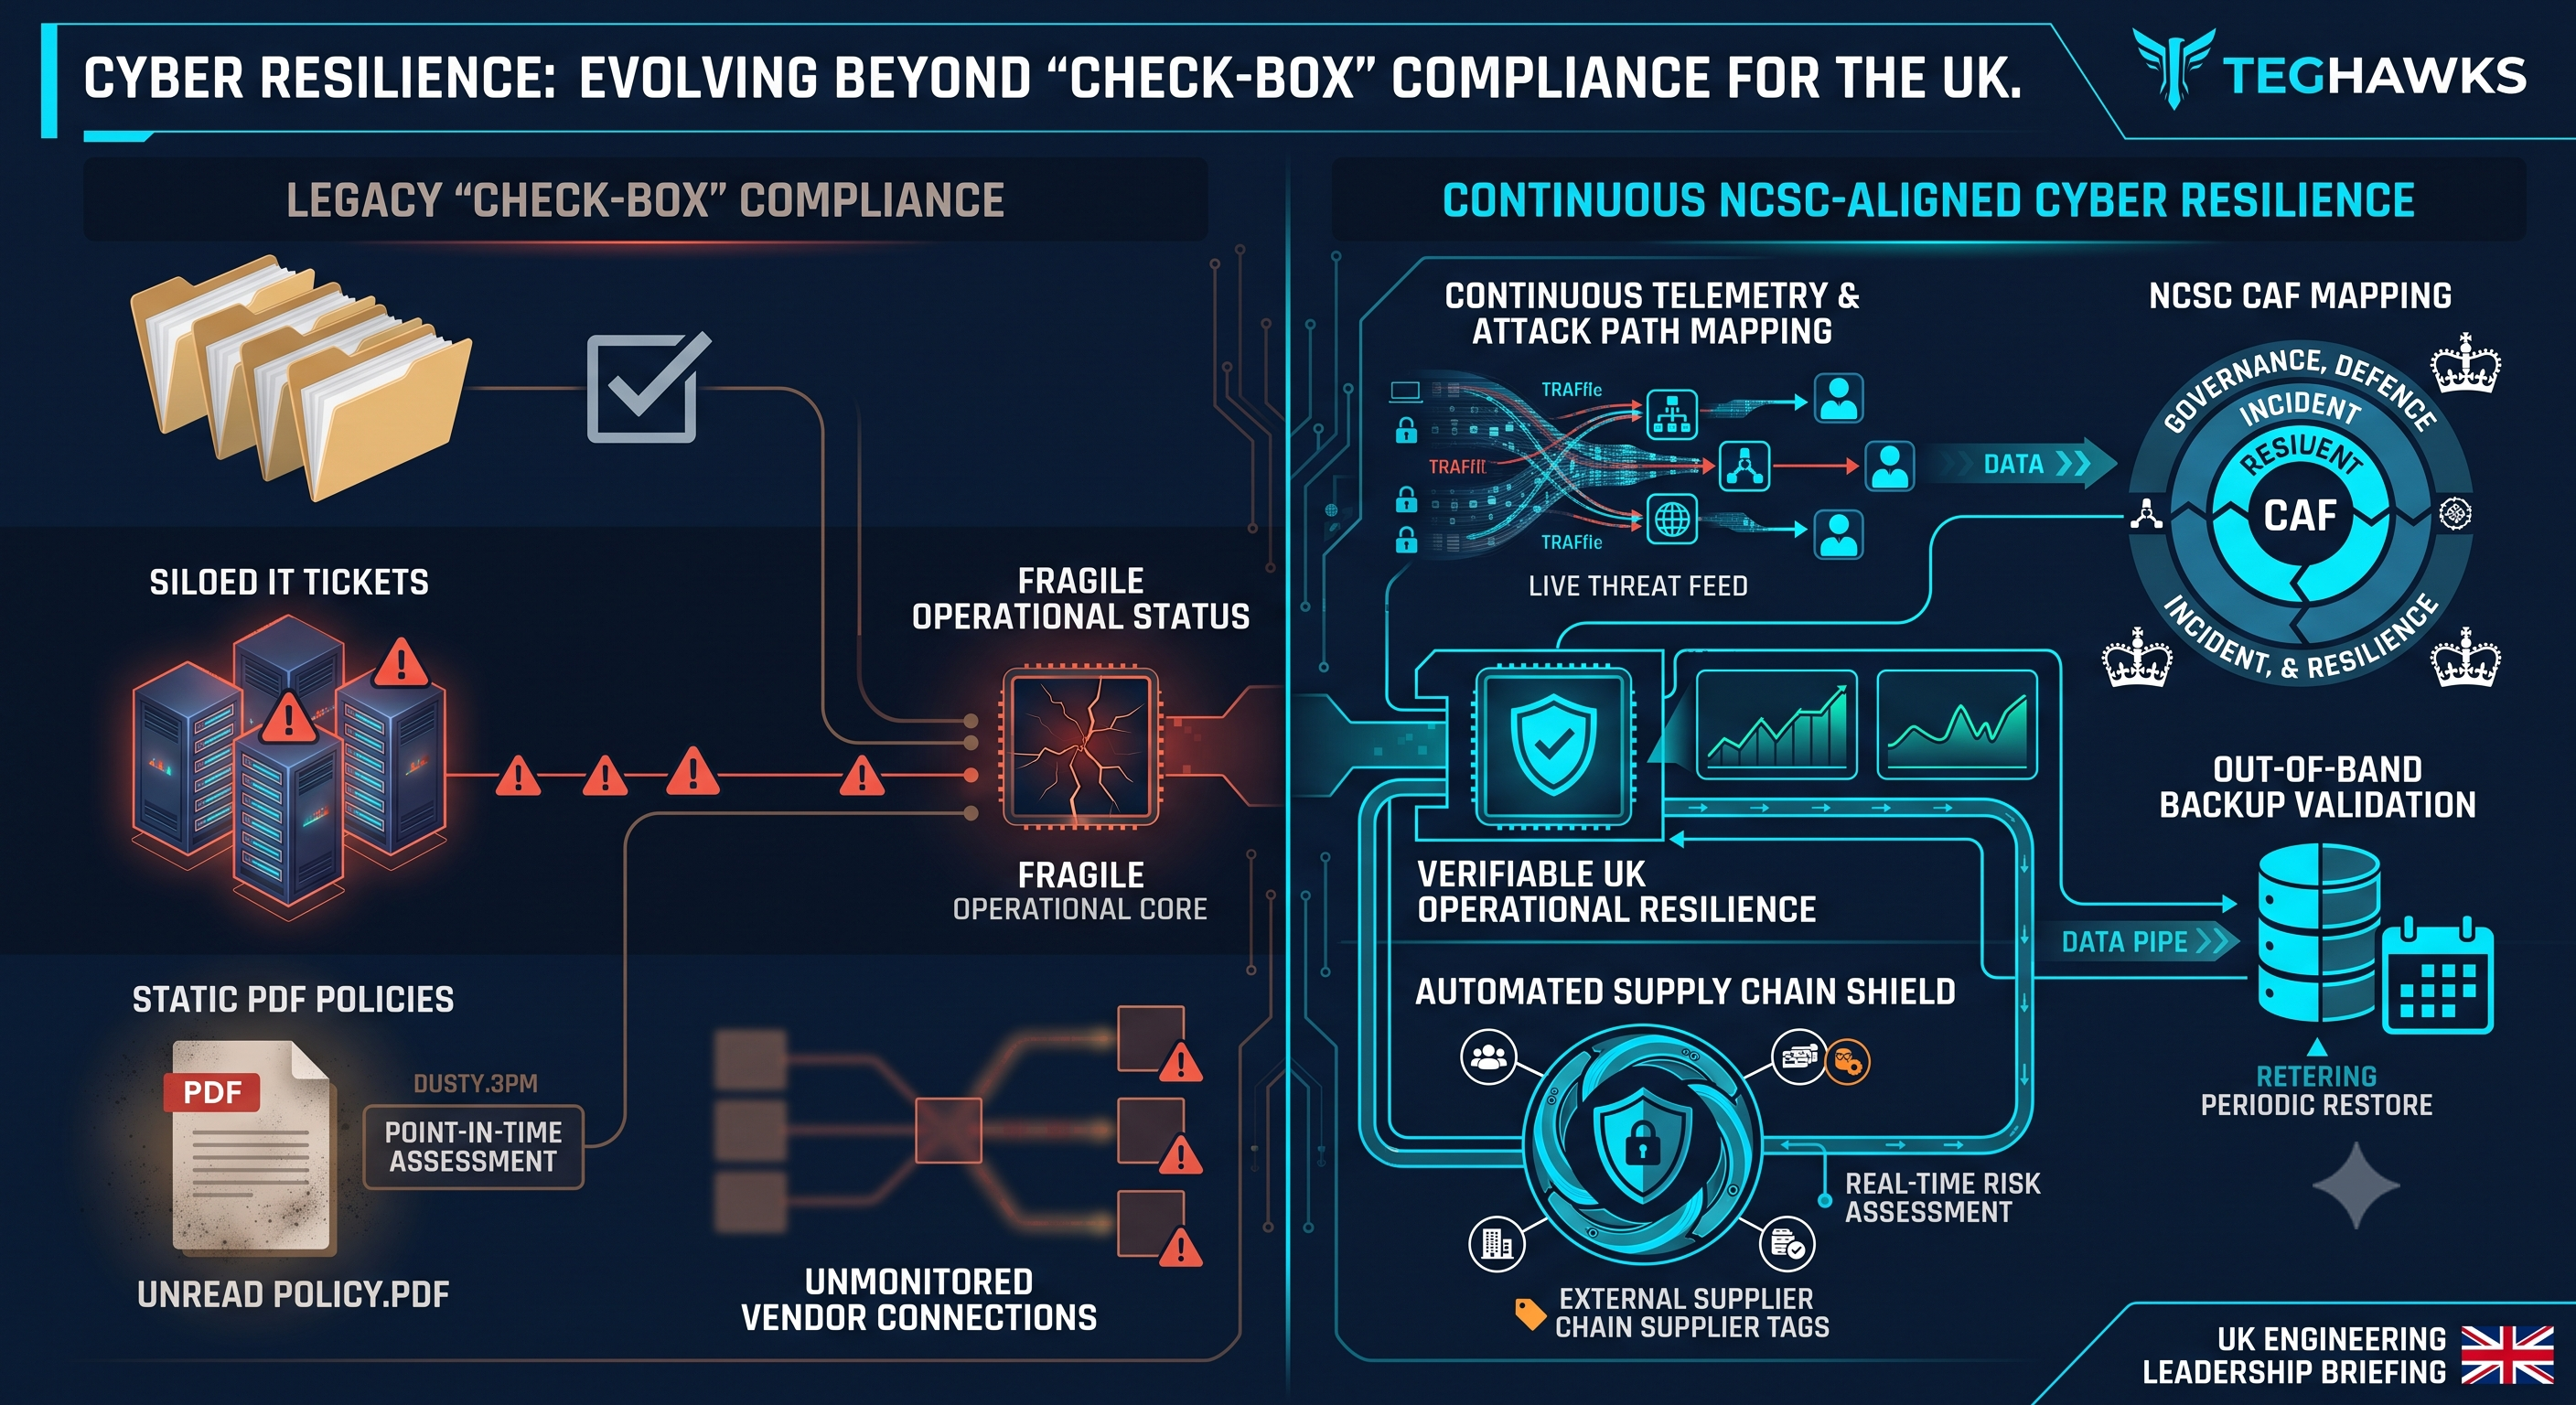
UK digital leadership is undergoing an aggressive regulatory pivot. With the Cyber Security and Resilience Bill expanding the scope of the Network and Information Systems (NIS) framework across supply chains and critical digital infrastructure, British tech firms can no longer treat cybersecurity as a back-office IT ticket.
The shift is clear: Regulators, enterprise procurement boards, and the NCSC no longer ask if you have security policies written down. They ask if you can prove your systems will survive a catastrophic supply-chain outage or ransomware attempt without downing customer operations.
Before enterprise auditors and procurement vetting freeze your deployment pipeline, test your architecture against this UK Engineering Cyber Resilience Checklist:
[ ] NCSC Cyber Assessment Framework (CAF) Mapping: Have you benchmarked your core services, IAM tiers, and access boundaries directly against the CAF indicators rather than generic self-assessment questionnaires?
[ ] Continuous Supply-Chain Blast Radius Limiting: Are third-party vendor dependencies, CI/CD runners, and external SaaS connectors strictly isolated with zero-standing-privilege (ZSP) rules?
[ ] Documented RTO & RPO Proof: Can your team execute an immutable, out-of-band disaster recovery restore with verified RPO (Recovery Point Objective) and RTO (Recovery Time Objective) targets tested within the last six months?
[ ] NCSC Early Warning Integration: Is your infrastructure enrolled in the NCSC Early Warning service to catch indicators of compromise (IoCs) and compromised network assets automatically?
[ ] Board-Level Accountability Artifacts: Does your team maintain an auditable, continuously refreshed cyber risk register with a designated board or executive sponsor as outlined in the Cyber Governance Code of Practice?
[ ] Sub-Tier Supplier Verification: Do all tier-1 and tier-2 service providers handling sensitive operations hold valid Cyber Essentials Plus certification with contractual incident notification triggers within 24 hours?
Building high-availability tech in the UK is no longer just about 99.99% system uptime. It is about proving system survivability and governance under statutory scrutiny.
Discussion Question
With supply chain liability tightening under UK law, what is your engineering team’s biggest hurdle: vendor dependency isolation, out-of-band recovery testing, or audit-grade telemetry?
CTA
Join Techawks UK to connect with British engineering leaders, cloud architects, and security officers modernising resilient enterprise infrastructure.
UK digital leadership is undergoing an aggressive regulatory pivot. With the Cyber Security and Resilience Bill expanding the scope of the Network and Information Systems (NIS) framework across supply chains and critical digital infrastructure, British tech firms can no longer treat cybersecurity as a back-office IT ticket.
The shift is clear: Regulators, enterprise procurement boards, and the NCSC no longer ask if you have security policies written down. They ask if you can prove your systems will survive a catastrophic supply-chain outage or ransomware attempt without downing customer operations.
Before enterprise auditors and procurement vetting freeze your deployment pipeline, test your architecture against this UK Engineering Cyber Resilience Checklist:
[ ] NCSC Cyber Assessment Framework (CAF) Mapping: Have you benchmarked your core services, IAM tiers, and access boundaries directly against the CAF indicators rather than generic self-assessment questionnaires?
[ ] Continuous Supply-Chain Blast Radius Limiting: Are third-party vendor dependencies, CI/CD runners, and external SaaS connectors strictly isolated with zero-standing-privilege (ZSP) rules?
[ ] Documented RTO & RPO Proof: Can your team execute an immutable, out-of-band disaster recovery restore with verified RPO (Recovery Point Objective) and RTO (Recovery Time Objective) targets tested within the last six months?
[ ] NCSC Early Warning Integration: Is your infrastructure enrolled in the NCSC Early Warning service to catch indicators of compromise (IoCs) and compromised network assets automatically?
[ ] Board-Level Accountability Artifacts: Does your team maintain an auditable, continuously refreshed cyber risk register with a designated board or executive sponsor as outlined in the Cyber Governance Code of Practice?
[ ] Sub-Tier Supplier Verification: Do all tier-1 and tier-2 service providers handling sensitive operations hold valid Cyber Essentials Plus certification with contractual incident notification triggers within 24 hours?
Building high-availability tech in the UK is no longer just about 99.99% system uptime. It is about proving system survivability and governance under statutory scrutiny.
Discussion Question
With supply chain liability tightening under UK law, what is your engineering team’s biggest hurdle: vendor dependency isolation, out-of-band recovery testing, or audit-grade telemetry?
CTA
Join Techawks UK to connect with British engineering leaders, cloud architects, and security officers modernising resilient enterprise infrastructure.
The Cyber Security & Resilience Bill: Is Your UK Tech Stack Actually Audit-Ready?
UK digital leadership is undergoing an aggressive regulatory pivot. With the Cyber Security and Resilience Bill expanding the scope of the Network and Information Systems (NIS) framework across supply chains and critical digital infrastructure, British tech firms can no longer treat cybersecurity as a back-office IT ticket.
The shift is clear: Regulators, enterprise procurement boards, and the NCSC no longer ask if you have security policies written down. They ask if you can prove your systems will survive a catastrophic supply-chain outage or ransomware attempt without downing customer operations.
Before enterprise auditors and procurement vetting freeze your deployment pipeline, test your architecture against this UK Engineering Cyber Resilience Checklist:
[ ] NCSC Cyber Assessment Framework (CAF) Mapping: Have you benchmarked your core services, IAM tiers, and access boundaries directly against the CAF indicators rather than generic self-assessment questionnaires?
[ ] Continuous Supply-Chain Blast Radius Limiting: Are third-party vendor dependencies, CI/CD runners, and external SaaS connectors strictly isolated with zero-standing-privilege (ZSP) rules?
[ ] Documented RTO & RPO Proof: Can your team execute an immutable, out-of-band disaster recovery restore with verified RPO (Recovery Point Objective) and RTO (Recovery Time Objective) targets tested within the last six months?
[ ] NCSC Early Warning Integration: Is your infrastructure enrolled in the NCSC Early Warning service to catch indicators of compromise (IoCs) and compromised network assets automatically?
[ ] Board-Level Accountability Artifacts: Does your team maintain an auditable, continuously refreshed cyber risk register with a designated board or executive sponsor as outlined in the Cyber Governance Code of Practice?
[ ] Sub-Tier Supplier Verification: Do all tier-1 and tier-2 service providers handling sensitive operations hold valid Cyber Essentials Plus certification with contractual incident notification triggers within 24 hours?
Building high-availability tech in the UK is no longer just about 99.99% system uptime. It is about proving system survivability and governance under statutory scrutiny.
Discussion Question
With supply chain liability tightening under UK law, what is your engineering team’s biggest hurdle: vendor dependency isolation, out-of-band recovery testing, or audit-grade telemetry?
CTA
Join Techawks UK to connect with British engineering leaders, cloud architects, and security officers modernising resilient enterprise infrastructure.

 English
 French
 Spanish
 Portuguese
 Deutsch
 Turkish
 Dutch
 Italiano
 Russian
 Romaian
 Portuguese (Brazil)
 Greek