


UAE Sovereign Cloud & AI Governance: Is Your Tech Stack Audit-Ready?
With the consolidation of national oversight under the UAE Federal Authority for Artificial Intelligence and Data, the Emirates has transitioned from establishing high-level frameworks to active regulatory supervision.
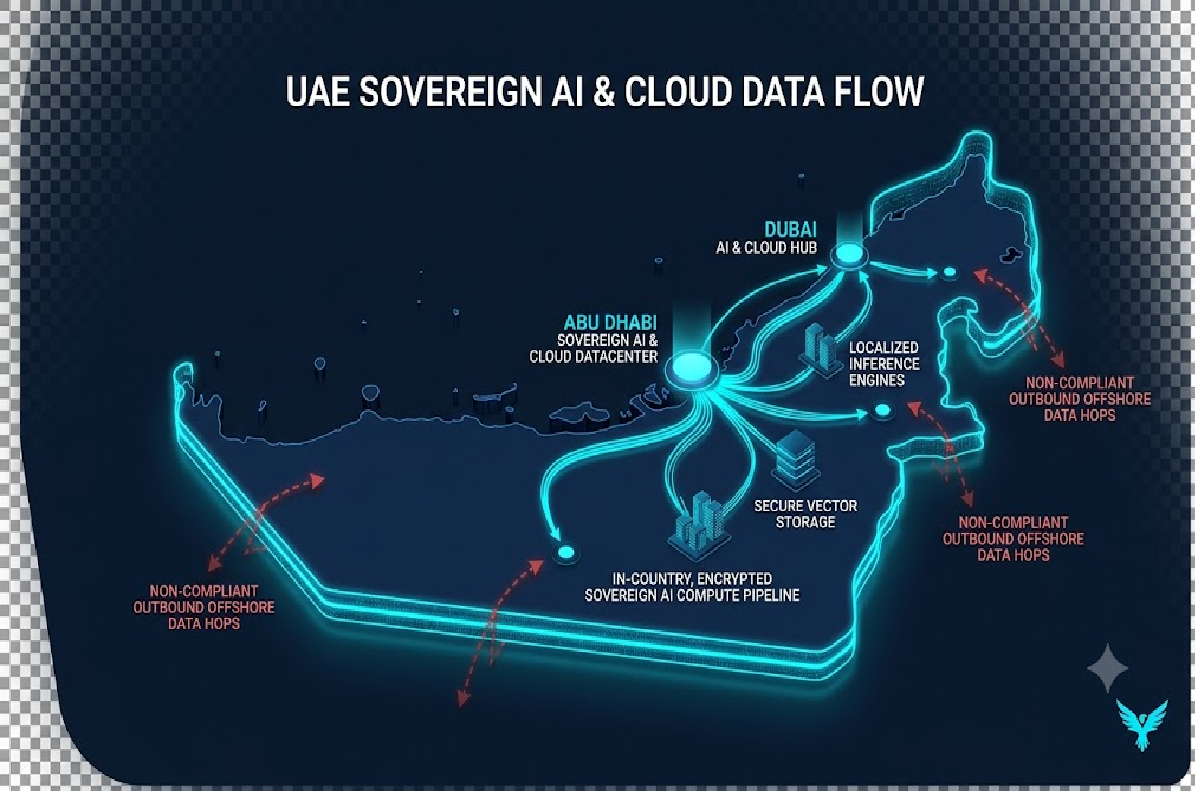
For CTOs, solutions architects, and engineering leaders operating across onshore UAE, DIFC, and ADGM, deploying AI workloads on offshore clouds without verifiable data residency is now an immediate governance liability.
Whether building agentic workflows, LLM pipelines, or multi-tenant SaaS, enterprise engineering teams must evaluate their systems against this UAE Sovereign Data & AI Architecture Checklist:
[ ] Data Residency & Boundary Enforcement: Are all customer personal identifiable information (PII) and training datasets ingested, processed, and retained within UAE borders (e.g., local sovereign cloud regions) to satisfy onshore Federal Decree-Law No. 45/2021 (PDPL) requirements?
[ ] Free Zone Regime Interoperability: If operating across DIFC or ADGM, does your AI deployment satisfy jurisdiction-specific requirements—such as DIFC Regulation 10 covering semi-autonomous and autonomous systems processing personal data?
[ ] Cross-Border Transfer Impact Assessments (TIAs): For systems leveraging offshore foundation models or APIs, do you have documented standard contractual clauses (SCCs) and transfer assessments justifying cross-border telemetry and payload routing?
[ ] Algorithmic Accountability & Explainability: Can your system output deterministic audit logs explaining model inference, guardrails, and decision pathways to satisfy sectoral requirements (such as CBUAE AI/ML guidance for financial workloads)?
[ ] Model Kill-Switch & Human-in-the-Loop Controls: Are operational overrides, circuit breakers, and human-in-the-loop validation active for automated workflows that execute critical actions or interface with public-facing digital services?
[ ] Sovereign Model Weight Isolation: If deploying fine-tuned or open-source weights (e.g., Falcon series), are model checkpoints and vector stores isolated from unauthorized third-party telemetry scraping?
Building in the UAE means moving at the frontier of innovation, but the regional winners will be those who design compliant, sovereign architectures from day one.
Discussion Question
As UAE data oversight unifies, what is your team's biggest hurdle: localising vector database residency, managing multi-jurisdiction compliance (Onshore vs. DIFC/ADGM), or setting up explainability audit trails?
CTA
Join Techawks UAE to connect with regional engineering leaders, enterprise cloud architects, and tech innovators architecting the future of sovereign Middle Eastern tech.
With the consolidation of national oversight under the UAE Federal Authority for Artificial Intelligence and Data, the Emirates has transitioned from establishing high-level frameworks to active regulatory supervision.
For CTOs, solutions architects, and engineering leaders operating across onshore UAE, DIFC, and ADGM, deploying AI workloads on offshore clouds without verifiable data residency is now an immediate governance liability.
Whether building agentic workflows, LLM pipelines, or multi-tenant SaaS, enterprise engineering teams must evaluate their systems against this UAE Sovereign Data & AI Architecture Checklist:
[ ] Data Residency & Boundary Enforcement: Are all customer personal identifiable information (PII) and training datasets ingested, processed, and retained within UAE borders (e.g., local sovereign cloud regions) to satisfy onshore Federal Decree-Law No. 45/2021 (PDPL) requirements?
[ ] Free Zone Regime Interoperability: If operating across DIFC or ADGM, does your AI deployment satisfy jurisdiction-specific requirements—such as DIFC Regulation 10 covering semi-autonomous and autonomous systems processing personal data?
[ ] Cross-Border Transfer Impact Assessments (TIAs): For systems leveraging offshore foundation models or APIs, do you have documented standard contractual clauses (SCCs) and transfer assessments justifying cross-border telemetry and payload routing?
[ ] Algorithmic Accountability & Explainability: Can your system output deterministic audit logs explaining model inference, guardrails, and decision pathways to satisfy sectoral requirements (such as CBUAE AI/ML guidance for financial workloads)?
[ ] Model Kill-Switch & Human-in-the-Loop Controls: Are operational overrides, circuit breakers, and human-in-the-loop validation active for automated workflows that execute critical actions or interface with public-facing digital services?
[ ] Sovereign Model Weight Isolation: If deploying fine-tuned or open-source weights (e.g., Falcon series), are model checkpoints and vector stores isolated from unauthorized third-party telemetry scraping?
Building in the UAE means moving at the frontier of innovation, but the regional winners will be those who design compliant, sovereign architectures from day one.
Discussion Question
As UAE data oversight unifies, what is your team's biggest hurdle: localising vector database residency, managing multi-jurisdiction compliance (Onshore vs. DIFC/ADGM), or setting up explainability audit trails?
CTA
Join Techawks UAE to connect with regional engineering leaders, enterprise cloud architects, and tech innovators architecting the future of sovereign Middle Eastern tech.
UAE Sovereign Cloud & AI Governance: Is Your Tech Stack Audit-Ready?
With the consolidation of national oversight under the UAE Federal Authority for Artificial Intelligence and Data, the Emirates has transitioned from establishing high-level frameworks to active regulatory supervision.
For CTOs, solutions architects, and engineering leaders operating across onshore UAE, DIFC, and ADGM, deploying AI workloads on offshore clouds without verifiable data residency is now an immediate governance liability.
Whether building agentic workflows, LLM pipelines, or multi-tenant SaaS, enterprise engineering teams must evaluate their systems against this UAE Sovereign Data & AI Architecture Checklist:
[ ] Data Residency & Boundary Enforcement: Are all customer personal identifiable information (PII) and training datasets ingested, processed, and retained within UAE borders (e.g., local sovereign cloud regions) to satisfy onshore Federal Decree-Law No. 45/2021 (PDPL) requirements?
[ ] Free Zone Regime Interoperability: If operating across DIFC or ADGM, does your AI deployment satisfy jurisdiction-specific requirements—such as DIFC Regulation 10 covering semi-autonomous and autonomous systems processing personal data?
[ ] Cross-Border Transfer Impact Assessments (TIAs): For systems leveraging offshore foundation models or APIs, do you have documented standard contractual clauses (SCCs) and transfer assessments justifying cross-border telemetry and payload routing?
[ ] Algorithmic Accountability & Explainability: Can your system output deterministic audit logs explaining model inference, guardrails, and decision pathways to satisfy sectoral requirements (such as CBUAE AI/ML guidance for financial workloads)?
[ ] Model Kill-Switch & Human-in-the-Loop Controls: Are operational overrides, circuit breakers, and human-in-the-loop validation active for automated workflows that execute critical actions or interface with public-facing digital services?
[ ] Sovereign Model Weight Isolation: If deploying fine-tuned or open-source weights (e.g., Falcon series), are model checkpoints and vector stores isolated from unauthorized third-party telemetry scraping?
Building in the UAE means moving at the frontier of innovation, but the regional winners will be those who design compliant, sovereign architectures from day one.
Discussion Question
As UAE data oversight unifies, what is your team's biggest hurdle: localising vector database residency, managing multi-jurisdiction compliance (Onshore vs. DIFC/ADGM), or setting up explainability audit trails?
CTA
Join Techawks UAE to connect with regional engineering leaders, enterprise cloud architects, and tech innovators architecting the future of sovereign Middle Eastern tech.

 English
 French
 Spanish
 Portuguese
 Deutsch
 Turkish
 Dutch
 Italiano
 Russian
 Romaian
 Portuguese (Brazil)
 Greek