


Why Bill C-26 (CCSPA) Just Obliterated the Traditional Canadian Tech Supply Chain
For years, Canadian software teams relied on a standard compliance playbook: pass a SOC 2 Type II audit, complete an annual vendor questionnaire, and host data in ca-central-1 to satisfy PIPEDA.
Under the CCSPA regime, that defensive perimeter is obsolete.
The framework gives regulators direct statutory power to mandate cybersecurity programs, order the immediate removal of high-risk third-party technologies, and impose penalties reaching up to $15 million per day. Crucially, designated operators (in finance, telecom, interprovincial transport, and energy) are legally required to mitigate cyber risks stemming from their third-party supply chains.
If your software sits in the dependency tree of a federally regulated Canadian enterprise, your CI/CD pipeline and open-source ingestion models are now subject to critical infrastructure audits.
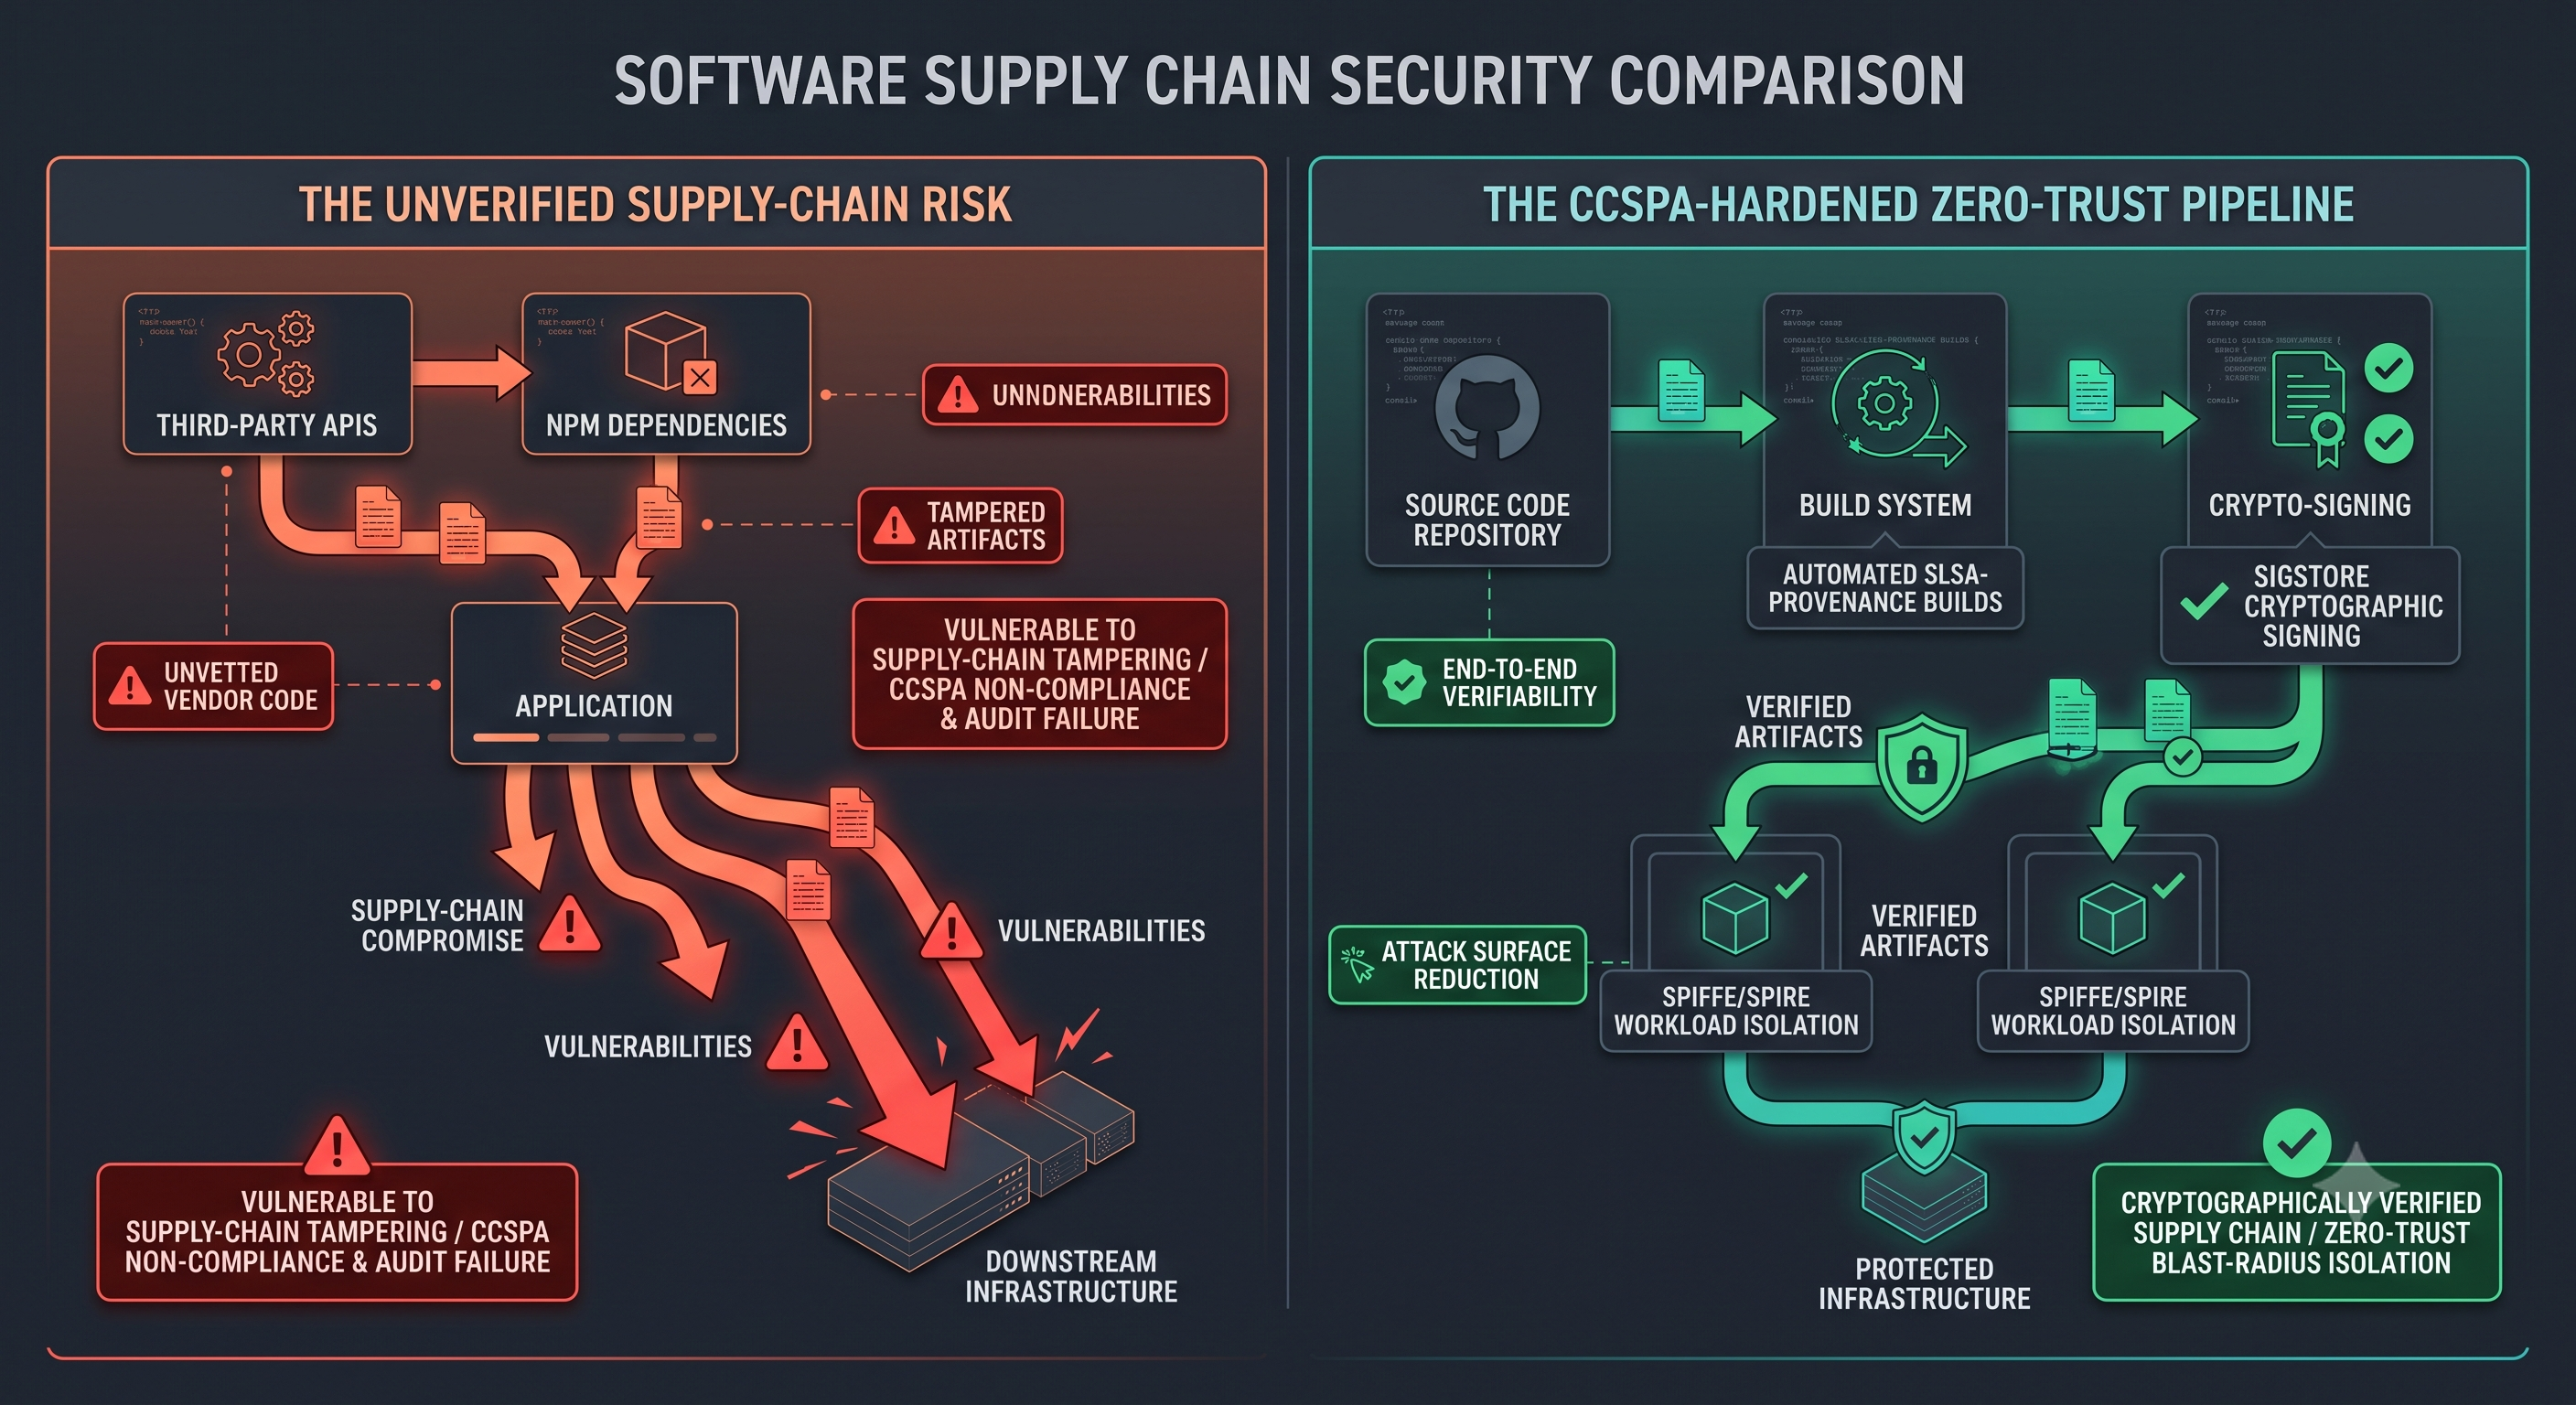
How engineering teams must re-architect for CCSPA supply-chain compliance:
Cryptographic Attestations via SLSA (Supply-chain Levels for Software Artifacts): Stop treating container builds and npm/PyPI dependencies as trusted by default. Implement automated provenance generation at build time using Sigstore/Cosign. Every container image and microservice binary deployed must cryptographically prove its source commit, build runner, and un-tampered integrity.
Granular Third-Party Blast Radius Isolation: In a microservices mesh, third-party integrations (APIs, webhooks, shared libraries) must be quarantined behind strict Zero-Trust egress proxies. Enforce least-privilege service-to-service communication with dynamic mutual TLS (mTLS) and fine-grained SPIFFE/SPIRE workload identities so a compromised vendor SDK cannot pivot into the core transaction plane.
Automated Runtime Vulnerability & Dependency Tracing: Static dependencies change constantly in production. Deploy continuous eBPF-based runtime monitoring to detect anomalous system calls, unexpected socket connections, or unexpected binary modifications introduced via automated dependency updates.
Discussion Question
If a Canadian tier-1 bank or telco customer triggered a CCSPA audit on your software tomorrow morning, could you provide end-to-end cryptographic proof of every third-party component running in your production cluster?
CTA
Master high-assurance software engineering and mission-critical cloud architecture. Join Techawks Canada to collaborate with senior SREs, systems architects, and security engineers from across the Canadian tech ecosystem.
For years, Canadian software teams relied on a standard compliance playbook: pass a SOC 2 Type II audit, complete an annual vendor questionnaire, and host data in ca-central-1 to satisfy PIPEDA.
Under the CCSPA regime, that defensive perimeter is obsolete.
The framework gives regulators direct statutory power to mandate cybersecurity programs, order the immediate removal of high-risk third-party technologies, and impose penalties reaching up to $15 million per day. Crucially, designated operators (in finance, telecom, interprovincial transport, and energy) are legally required to mitigate cyber risks stemming from their third-party supply chains.
If your software sits in the dependency tree of a federally regulated Canadian enterprise, your CI/CD pipeline and open-source ingestion models are now subject to critical infrastructure audits.
How engineering teams must re-architect for CCSPA supply-chain compliance:
Cryptographic Attestations via SLSA (Supply-chain Levels for Software Artifacts): Stop treating container builds and npm/PyPI dependencies as trusted by default. Implement automated provenance generation at build time using Sigstore/Cosign. Every container image and microservice binary deployed must cryptographically prove its source commit, build runner, and un-tampered integrity.
Granular Third-Party Blast Radius Isolation: In a microservices mesh, third-party integrations (APIs, webhooks, shared libraries) must be quarantined behind strict Zero-Trust egress proxies. Enforce least-privilege service-to-service communication with dynamic mutual TLS (mTLS) and fine-grained SPIFFE/SPIRE workload identities so a compromised vendor SDK cannot pivot into the core transaction plane.
Automated Runtime Vulnerability & Dependency Tracing: Static dependencies change constantly in production. Deploy continuous eBPF-based runtime monitoring to detect anomalous system calls, unexpected socket connections, or unexpected binary modifications introduced via automated dependency updates.
Discussion Question
If a Canadian tier-1 bank or telco customer triggered a CCSPA audit on your software tomorrow morning, could you provide end-to-end cryptographic proof of every third-party component running in your production cluster?
CTA
Master high-assurance software engineering and mission-critical cloud architecture. Join Techawks Canada to collaborate with senior SREs, systems architects, and security engineers from across the Canadian tech ecosystem.
Why Bill C-26 (CCSPA) Just Obliterated the Traditional Canadian Tech Supply Chain
For years, Canadian software teams relied on a standard compliance playbook: pass a SOC 2 Type II audit, complete an annual vendor questionnaire, and host data in ca-central-1 to satisfy PIPEDA.
Under the CCSPA regime, that defensive perimeter is obsolete.
The framework gives regulators direct statutory power to mandate cybersecurity programs, order the immediate removal of high-risk third-party technologies, and impose penalties reaching up to $15 million per day. Crucially, designated operators (in finance, telecom, interprovincial transport, and energy) are legally required to mitigate cyber risks stemming from their third-party supply chains.
If your software sits in the dependency tree of a federally regulated Canadian enterprise, your CI/CD pipeline and open-source ingestion models are now subject to critical infrastructure audits.
How engineering teams must re-architect for CCSPA supply-chain compliance:
Cryptographic Attestations via SLSA (Supply-chain Levels for Software Artifacts): Stop treating container builds and npm/PyPI dependencies as trusted by default. Implement automated provenance generation at build time using Sigstore/Cosign. Every container image and microservice binary deployed must cryptographically prove its source commit, build runner, and un-tampered integrity.
Granular Third-Party Blast Radius Isolation: In a microservices mesh, third-party integrations (APIs, webhooks, shared libraries) must be quarantined behind strict Zero-Trust egress proxies. Enforce least-privilege service-to-service communication with dynamic mutual TLS (mTLS) and fine-grained SPIFFE/SPIRE workload identities so a compromised vendor SDK cannot pivot into the core transaction plane.
Automated Runtime Vulnerability & Dependency Tracing: Static dependencies change constantly in production. Deploy continuous eBPF-based runtime monitoring to detect anomalous system calls, unexpected socket connections, or unexpected binary modifications introduced via automated dependency updates.
Discussion Question
If a Canadian tier-1 bank or telco customer triggered a CCSPA audit on your software tomorrow morning, could you provide end-to-end cryptographic proof of every third-party component running in your production cluster?
CTA
Master high-assurance software engineering and mission-critical cloud architecture. Join Techawks Canada to collaborate with senior SREs, systems architects, and security engineers from across the Canadian tech ecosystem.

 English
 Arabic
 French
 Spanish
 Portuguese
 Deutsch
 Turkish
 Dutch
 Russian
 Romaian
 Portuguese (Brazil)
 Greek