


The DPDP Compliance Mirage: Why a Privacy Policy Update Won’t Save Indian Startups from ₹250 Crore Penalties
Across the Indian tech ecosystem—from Bengaluru SaaS ventures to Mumbai fintechs—a dangerous misconception has set in:
❌ The Myth: "DPDP compliance is a legal check-the-box exercise. Just update terms, publish a grievance officer email, and show a 'By signing up, you agree' consent banner."
✅ The Reality: India’s Digital Personal Data Protection framework strictly bans bundled consent, pre-ticked checkboxes, and unconditional terms of service. True compliance requires granular consent ledgers, purpose-limited data lifecycles, and automated Right-to-Erasure workflows.
Where Legacy Indian Tech Architectures Will Break:
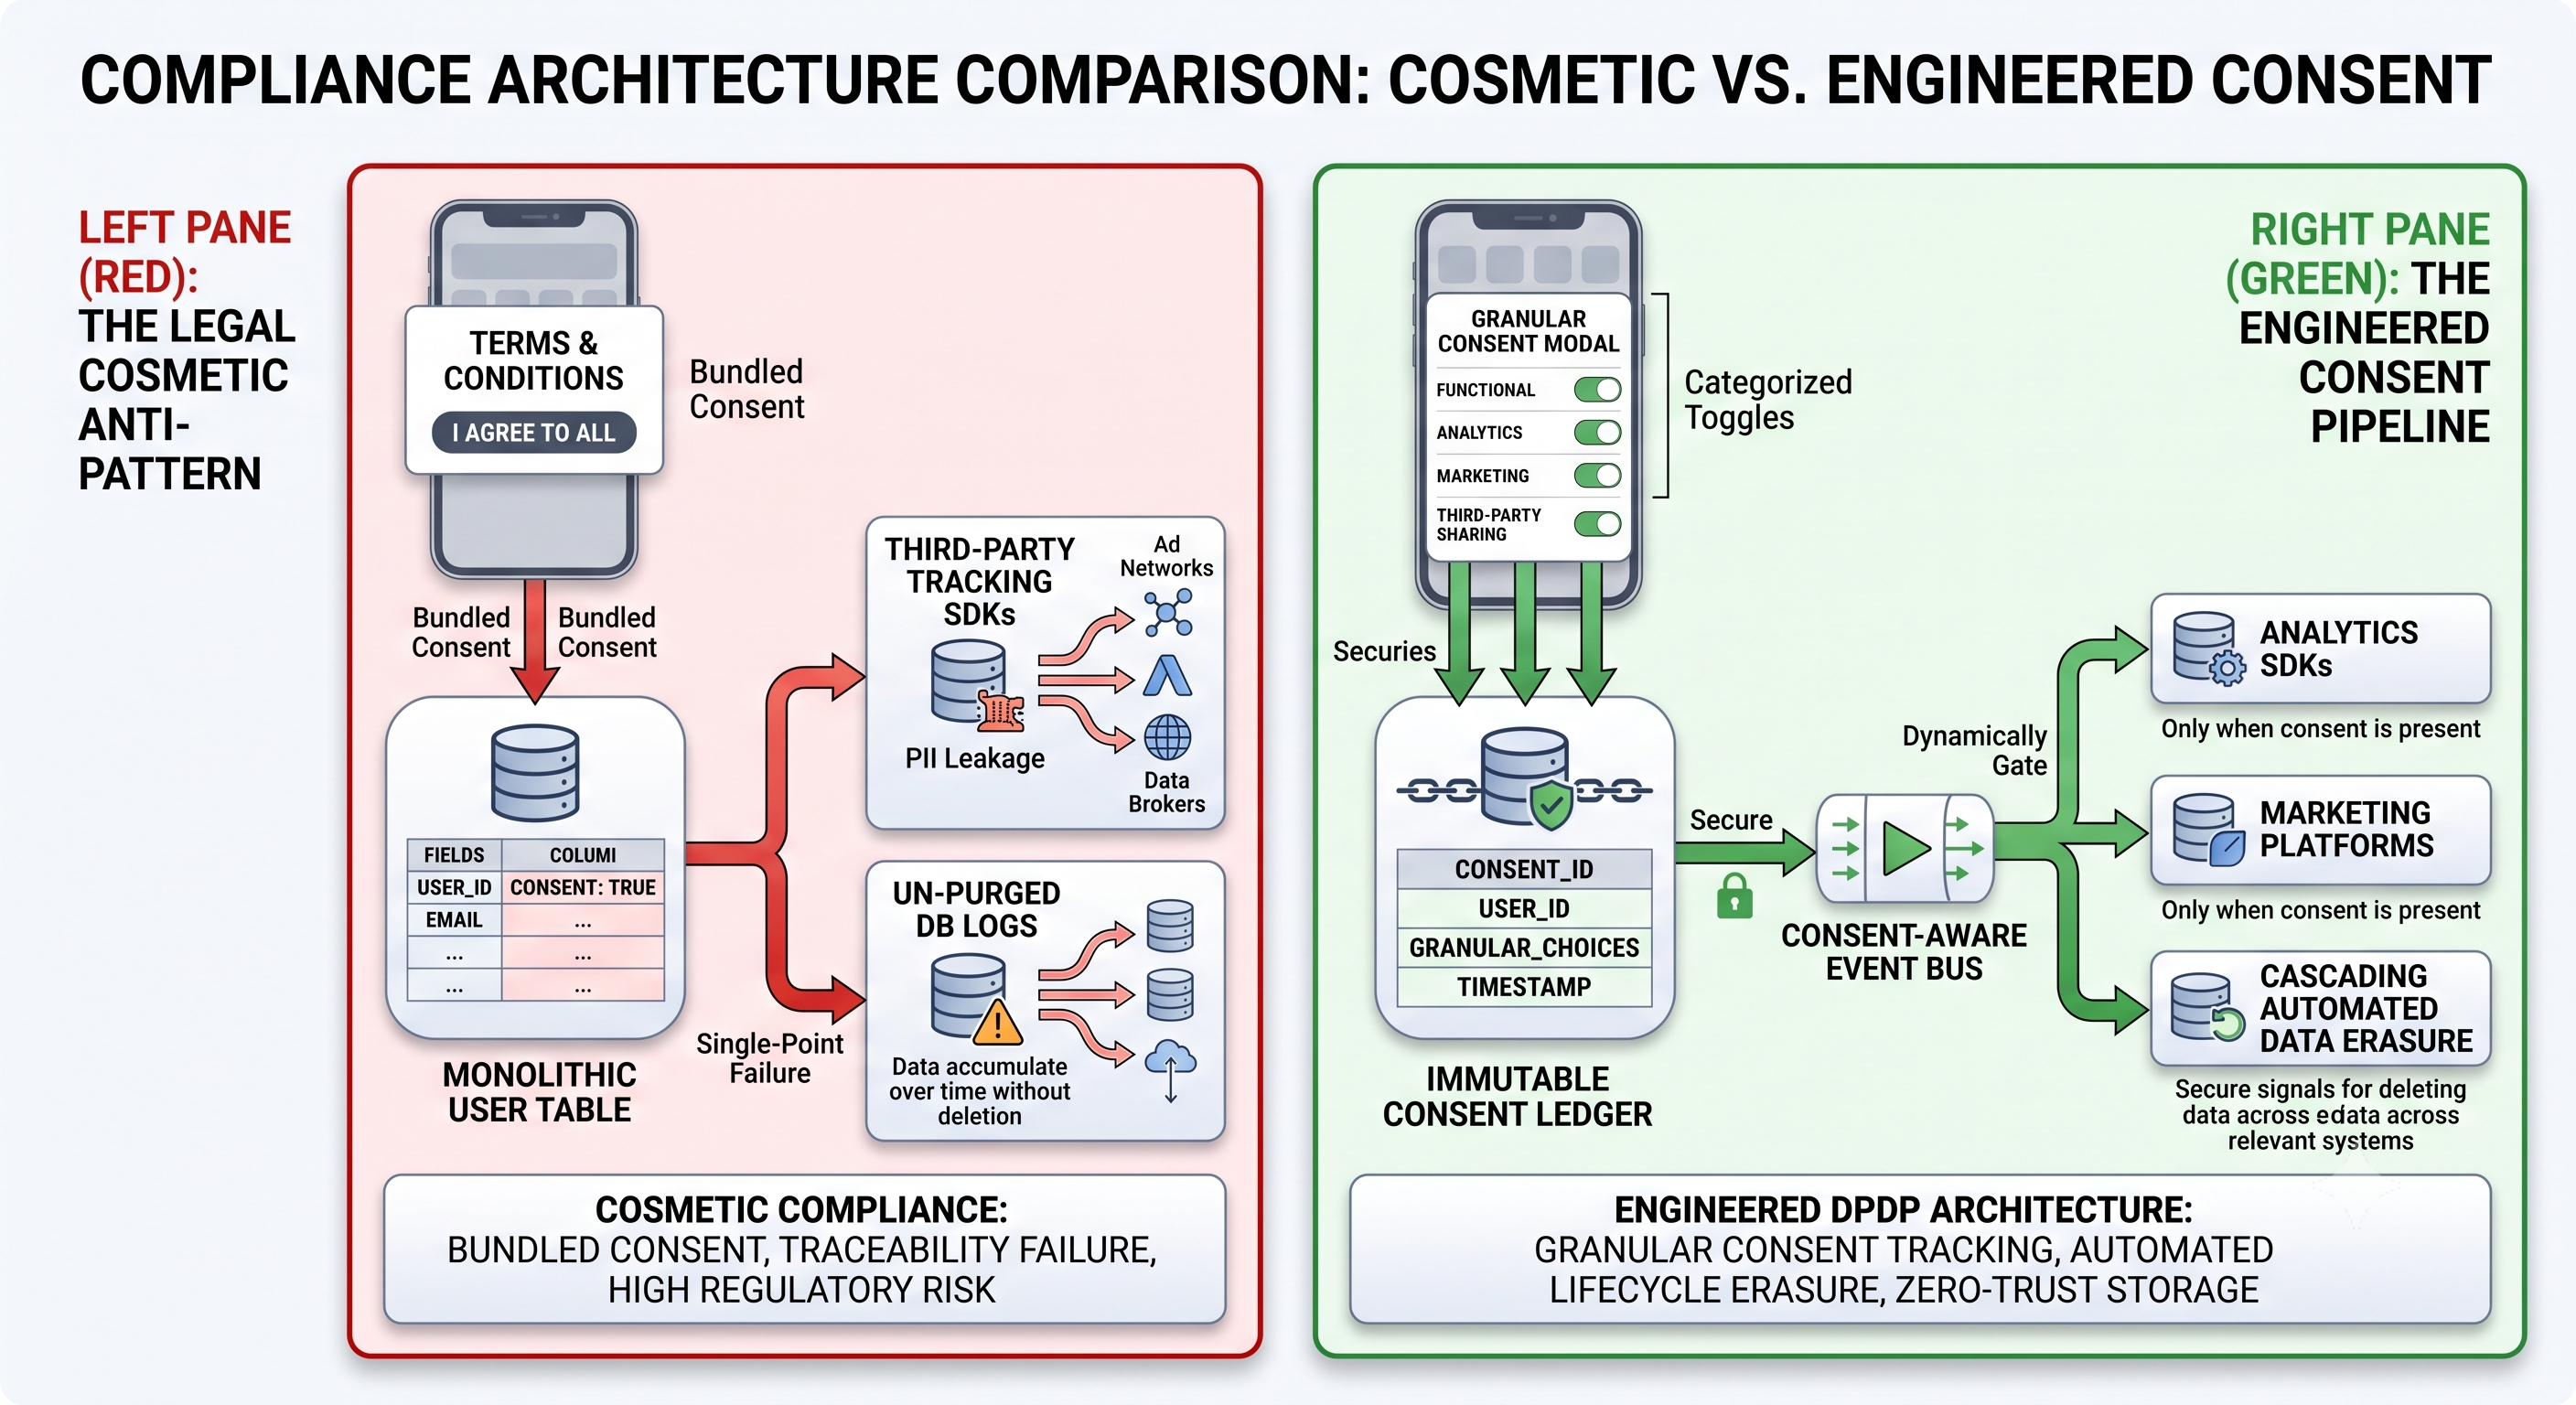
The Single-Boolean Consent Flaw: Storing is_consent_given = true on your users table will fail compliance scrutiny. The law mandates granular, unbundled consent across specific processing purposes (e.g., core fulfillment vs. promotional analytics vs. third-party SDK sharing). If challenged, you must provide verifiable proof of the exact policy version and granular permissions granted at that timestamp.
The "Soft-Delete" Illusion: In most Indian codebases, user deletion is merely setting is_deleted = true. Under DPDP’s Right to Erasure, holding plaintext personally identifiable information (PII) indefinitely across transaction logs, read replicas, and vector embeddings without an ongoing lawful purpose creates direct legal exposure.
Third-Party Telemetry Leaks: When an app initializes third-party analytics, crash reporting, or advertising SDKs before explicit consent is granted, customer PII and device fingerprints get transmitted externally. Under the Act, the data fiduciary remains strictly liable for processors down the pipeline.
The Engineering Blueprint for DPDP Readiness:
Build an Immutable Consent Ledger: Implement a dedicated event log tracking User_ID, Purpose_Category, Policy_Version_Hash, and Timestamp. Every state change (opt-in or revocation) must publish an event to message brokers.
Implement Dynamic Feature Gating: Decouple third-party trackers and non-essential APIs from initial app boot. Gate non-essential SDK network calls behind dynamic consent flags queried at runtime.
Automate Cascading Erasure Pipelines: Build asynchronous workers (Kafka/SQS) that listen for withdrawal/deletion events to purge or irreversibly cryptographically tokenize customer PII across caching layers, data warehouses, and downstream microservices.
The takeaway: A privacy policy written by a top law firm cannot compensate for an un-auditable database. If your engineering schema cannot programmatically trace and revoke consent per data field, your platform remains exposed.
Discussion Question
Has your team audited third-party analytics and ad SDKs for DPDP compliance, or are trackers still firing before explicit user consent is registered?
CTA (Join Techawks India)
Join Techawks India to discuss local engineering regulations, dissect sovereign tech architectures, and scale resilient products with India’s leading technologists.
Across the Indian tech ecosystem—from Bengaluru SaaS ventures to Mumbai fintechs—a dangerous misconception has set in:
❌ The Myth: "DPDP compliance is a legal check-the-box exercise. Just update terms, publish a grievance officer email, and show a 'By signing up, you agree' consent banner."
✅ The Reality: India’s Digital Personal Data Protection framework strictly bans bundled consent, pre-ticked checkboxes, and unconditional terms of service. True compliance requires granular consent ledgers, purpose-limited data lifecycles, and automated Right-to-Erasure workflows.
Where Legacy Indian Tech Architectures Will Break:
The Single-Boolean Consent Flaw: Storing is_consent_given = true on your users table will fail compliance scrutiny. The law mandates granular, unbundled consent across specific processing purposes (e.g., core fulfillment vs. promotional analytics vs. third-party SDK sharing). If challenged, you must provide verifiable proof of the exact policy version and granular permissions granted at that timestamp.
The "Soft-Delete" Illusion: In most Indian codebases, user deletion is merely setting is_deleted = true. Under DPDP’s Right to Erasure, holding plaintext personally identifiable information (PII) indefinitely across transaction logs, read replicas, and vector embeddings without an ongoing lawful purpose creates direct legal exposure.
Third-Party Telemetry Leaks: When an app initializes third-party analytics, crash reporting, or advertising SDKs before explicit consent is granted, customer PII and device fingerprints get transmitted externally. Under the Act, the data fiduciary remains strictly liable for processors down the pipeline.
The Engineering Blueprint for DPDP Readiness:
Build an Immutable Consent Ledger: Implement a dedicated event log tracking User_ID, Purpose_Category, Policy_Version_Hash, and Timestamp. Every state change (opt-in or revocation) must publish an event to message brokers.
Implement Dynamic Feature Gating: Decouple third-party trackers and non-essential APIs from initial app boot. Gate non-essential SDK network calls behind dynamic consent flags queried at runtime.
Automate Cascading Erasure Pipelines: Build asynchronous workers (Kafka/SQS) that listen for withdrawal/deletion events to purge or irreversibly cryptographically tokenize customer PII across caching layers, data warehouses, and downstream microservices.
The takeaway: A privacy policy written by a top law firm cannot compensate for an un-auditable database. If your engineering schema cannot programmatically trace and revoke consent per data field, your platform remains exposed.
Discussion Question
Has your team audited third-party analytics and ad SDKs for DPDP compliance, or are trackers still firing before explicit user consent is registered?
CTA (Join Techawks India)
Join Techawks India to discuss local engineering regulations, dissect sovereign tech architectures, and scale resilient products with India’s leading technologists.
The DPDP Compliance Mirage: Why a Privacy Policy Update Won’t Save Indian Startups from ₹250 Crore Penalties
Across the Indian tech ecosystem—from Bengaluru SaaS ventures to Mumbai fintechs—a dangerous misconception has set in:
❌ The Myth: "DPDP compliance is a legal check-the-box exercise. Just update terms, publish a grievance officer email, and show a 'By signing up, you agree' consent banner."
✅ The Reality: India’s Digital Personal Data Protection framework strictly bans bundled consent, pre-ticked checkboxes, and unconditional terms of service. True compliance requires granular consent ledgers, purpose-limited data lifecycles, and automated Right-to-Erasure workflows.
Where Legacy Indian Tech Architectures Will Break:
The Single-Boolean Consent Flaw: Storing is_consent_given = true on your users table will fail compliance scrutiny. The law mandates granular, unbundled consent across specific processing purposes (e.g., core fulfillment vs. promotional analytics vs. third-party SDK sharing). If challenged, you must provide verifiable proof of the exact policy version and granular permissions granted at that timestamp.
The "Soft-Delete" Illusion: In most Indian codebases, user deletion is merely setting is_deleted = true. Under DPDP’s Right to Erasure, holding plaintext personally identifiable information (PII) indefinitely across transaction logs, read replicas, and vector embeddings without an ongoing lawful purpose creates direct legal exposure.
Third-Party Telemetry Leaks: When an app initializes third-party analytics, crash reporting, or advertising SDKs before explicit consent is granted, customer PII and device fingerprints get transmitted externally. Under the Act, the data fiduciary remains strictly liable for processors down the pipeline.
The Engineering Blueprint for DPDP Readiness:
Build an Immutable Consent Ledger: Implement a dedicated event log tracking User_ID, Purpose_Category, Policy_Version_Hash, and Timestamp. Every state change (opt-in or revocation) must publish an event to message brokers.
Implement Dynamic Feature Gating: Decouple third-party trackers and non-essential APIs from initial app boot. Gate non-essential SDK network calls behind dynamic consent flags queried at runtime.
Automate Cascading Erasure Pipelines: Build asynchronous workers (Kafka/SQS) that listen for withdrawal/deletion events to purge or irreversibly cryptographically tokenize customer PII across caching layers, data warehouses, and downstream microservices.
The takeaway: A privacy policy written by a top law firm cannot compensate for an un-auditable database. If your engineering schema cannot programmatically trace and revoke consent per data field, your platform remains exposed.
Discussion Question
Has your team audited third-party analytics and ad SDKs for DPDP compliance, or are trackers still firing before explicit user consent is registered?
CTA (Join Techawks India)
Join Techawks India to discuss local engineering regulations, dissect sovereign tech architectures, and scale resilient products with India’s leading technologists.

 English
 Arabic
 French
 Spanish
 Portuguese
 Deutsch
 Turkish
 Dutch
 Italiano
 Russian
 Romaian
 Portuguese (Brazil)