


The Hidden Tech Risk in Your UK Supply Chain: Why Third-Party Cyber Audits are the New Gold Standard
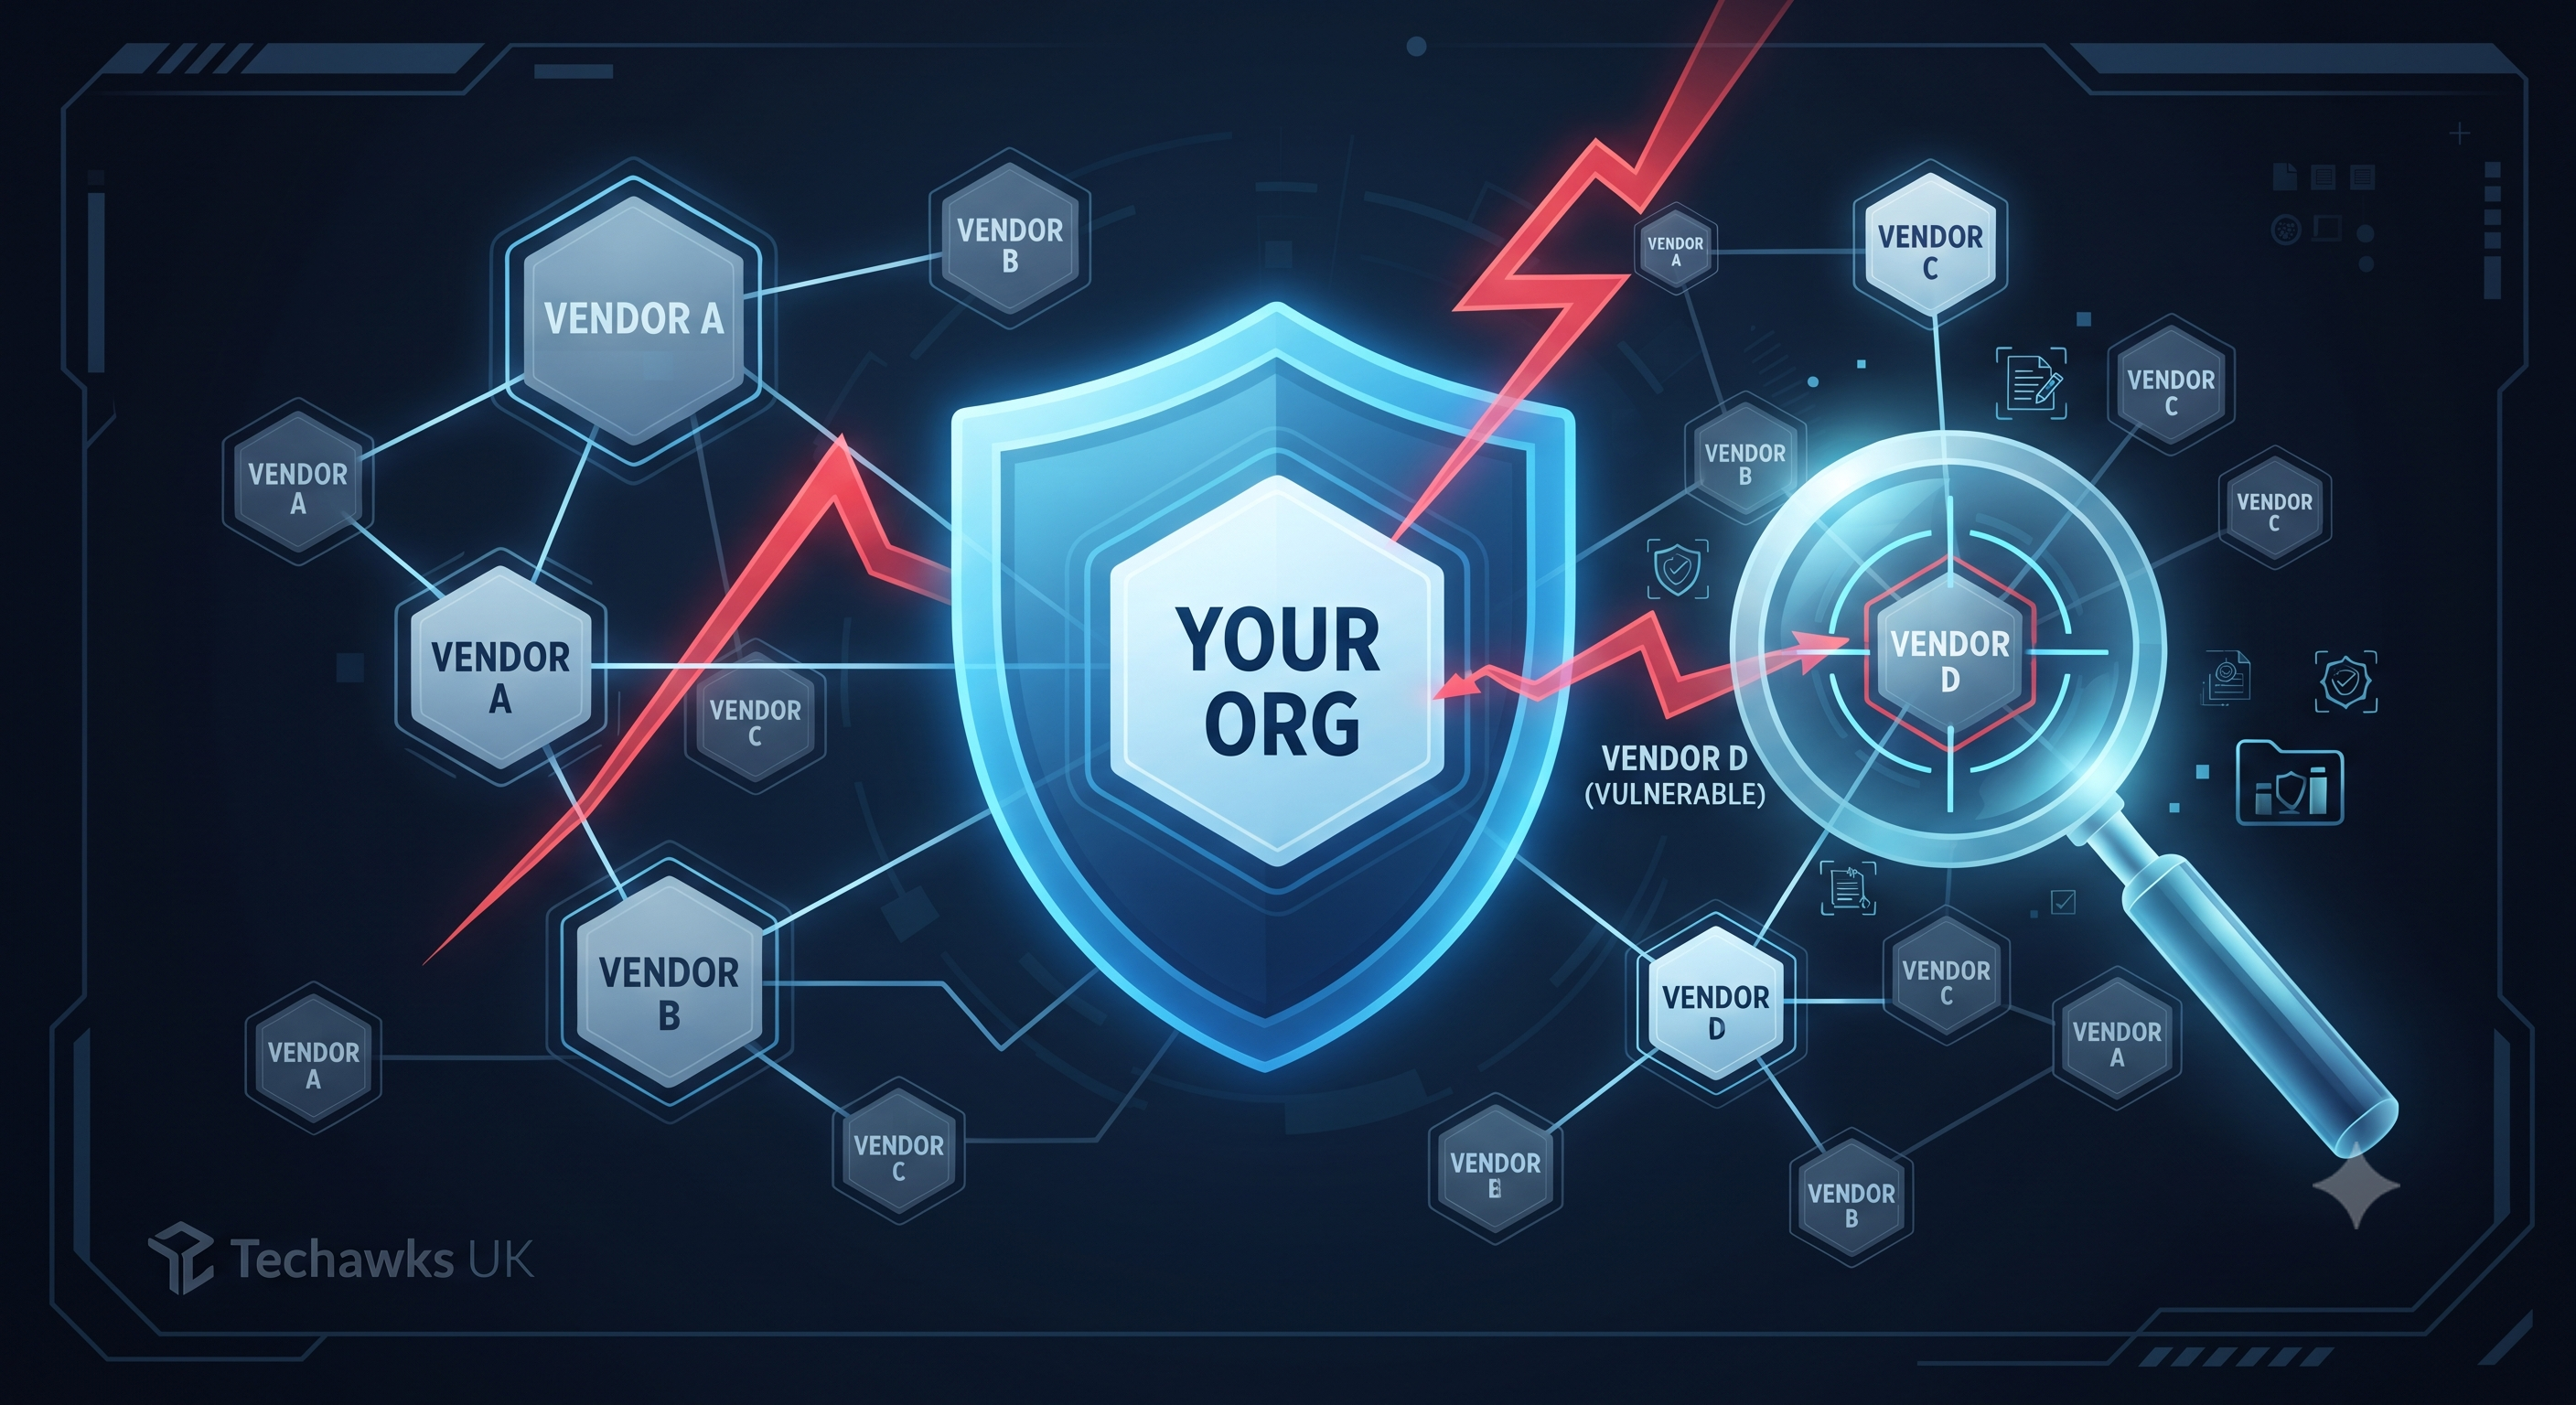
In today's interconnected ecosystem, nearly every UK business relies on third-party suppliers, from cloud providers and payroll processors to niche software vendors. However, recent UK cyber-threat intelligence reports indicate a significant rise in supply chain attacks, where malicious actors target the weakest link in the chain to gain access to larger, better-defended targets.
For UK tech leaders and security professionals, the responsibility extends beyond your own firewall. You are only as secure as your least secure vendor. Relying on a simple security questionnaire is no longer sufficient.
How to mature your third-party risk management (TPRM) process:
Tier Your Vendors: Do not audit everyone equally. Classify vendors based on the data they access and their criticality to your operations. A cloud host requires deeper scrutiny than a stationery supplier.
Request Actionable Evidence: Move beyond asking "Do you have a firewall?" to "Show me your last external penetration test report and how you remediated critical vulnerabilities."
Continuous Monitoring is Key: A vendor's security posture can change overnight. Implement continuous external attack surface monitoring to detect new vulnerabilities or exposed credentials in real-time, rather than relying on an annual review.
Securing the UK tech landscape requires a collective effort. Manage your risk, not just your network.
Discussion Question
What is the biggest challenge your team faces when trying to audit the security practices of smaller, less mature suppliers? Let’s share strategies below! 👇
CTA (Join Techawks UK)
Want to stay ahead of the evolving UK cyber threat landscape, connect with fellow security professionals, and access expert guidance on building resilient tech ecosystems?
👉 [Join Techawks UK today and secure the digital future with us.]
In today's interconnected ecosystem, nearly every UK business relies on third-party suppliers, from cloud providers and payroll processors to niche software vendors. However, recent UK cyber-threat intelligence reports indicate a significant rise in supply chain attacks, where malicious actors target the weakest link in the chain to gain access to larger, better-defended targets.
For UK tech leaders and security professionals, the responsibility extends beyond your own firewall. You are only as secure as your least secure vendor. Relying on a simple security questionnaire is no longer sufficient.
How to mature your third-party risk management (TPRM) process:
Tier Your Vendors: Do not audit everyone equally. Classify vendors based on the data they access and their criticality to your operations. A cloud host requires deeper scrutiny than a stationery supplier.
Request Actionable Evidence: Move beyond asking "Do you have a firewall?" to "Show me your last external penetration test report and how you remediated critical vulnerabilities."
Continuous Monitoring is Key: A vendor's security posture can change overnight. Implement continuous external attack surface monitoring to detect new vulnerabilities or exposed credentials in real-time, rather than relying on an annual review.
Securing the UK tech landscape requires a collective effort. Manage your risk, not just your network.
Discussion Question
What is the biggest challenge your team faces when trying to audit the security practices of smaller, less mature suppliers? Let’s share strategies below! 👇
CTA (Join Techawks UK)
Want to stay ahead of the evolving UK cyber threat landscape, connect with fellow security professionals, and access expert guidance on building resilient tech ecosystems?
👉 [Join Techawks UK today and secure the digital future with us.]
The Hidden Tech Risk in Your UK Supply Chain: Why Third-Party Cyber Audits are the New Gold Standard
In today's interconnected ecosystem, nearly every UK business relies on third-party suppliers, from cloud providers and payroll processors to niche software vendors. However, recent UK cyber-threat intelligence reports indicate a significant rise in supply chain attacks, where malicious actors target the weakest link in the chain to gain access to larger, better-defended targets.
For UK tech leaders and security professionals, the responsibility extends beyond your own firewall. You are only as secure as your least secure vendor. Relying on a simple security questionnaire is no longer sufficient.
How to mature your third-party risk management (TPRM) process:
Tier Your Vendors: Do not audit everyone equally. Classify vendors based on the data they access and their criticality to your operations. A cloud host requires deeper scrutiny than a stationery supplier.
Request Actionable Evidence: Move beyond asking "Do you have a firewall?" to "Show me your last external penetration test report and how you remediated critical vulnerabilities."
Continuous Monitoring is Key: A vendor's security posture can change overnight. Implement continuous external attack surface monitoring to detect new vulnerabilities or exposed credentials in real-time, rather than relying on an annual review.
Securing the UK tech landscape requires a collective effort. Manage your risk, not just your network.
Discussion Question
What is the biggest challenge your team faces when trying to audit the security practices of smaller, less mature suppliers? Let’s share strategies below! 👇
CTA (Join Techawks UK)
Want to stay ahead of the evolving UK cyber threat landscape, connect with fellow security professionals, and access expert guidance on building resilient tech ecosystems?
👉 [Join Techawks UK today and secure the digital future with us.]

 English
 Arabic
 French
 Spanish
 Portuguese
 Deutsch
 Turkish
 Dutch
 Italiano
 Romaian
 Portuguese (Brazil)
 Greek