


Navigating the Multi-Regime Maze: Building an AI Compliance Framework for UK Enterprises
As British organizations rapidly adopt agentic AI and automated decision systems, compliance has shifted from a legal checklist into a core engineering requirement. Operating in the UK tech market means navigating multiple parallel regimes—including UK GDPR, data use standards, sector-specific oversight, and the extraterritorial reach of EU rules for teams serving cross-border users.
When autonomous agents process personal data or influence financial, medical, or operational decisions, static policy documents are no longer enough. Regulators expect transparent, auditable, and resilient system behavior.
Why This Matters
If your AI governance strategy relies entirely on reactive reviews, you risk regulatory friction, operational downtime, and severe reputational damage. Building a proactive compliance framework ensures your engineering pipelines can scale safely while maintaining clear accountability across your technical stack.
Mini-Tutorial: Implementing an Engineering-Led Compliance Harness
Protect your UK-based deployments and streamline regulatory readiness by embedding these three technical controls:
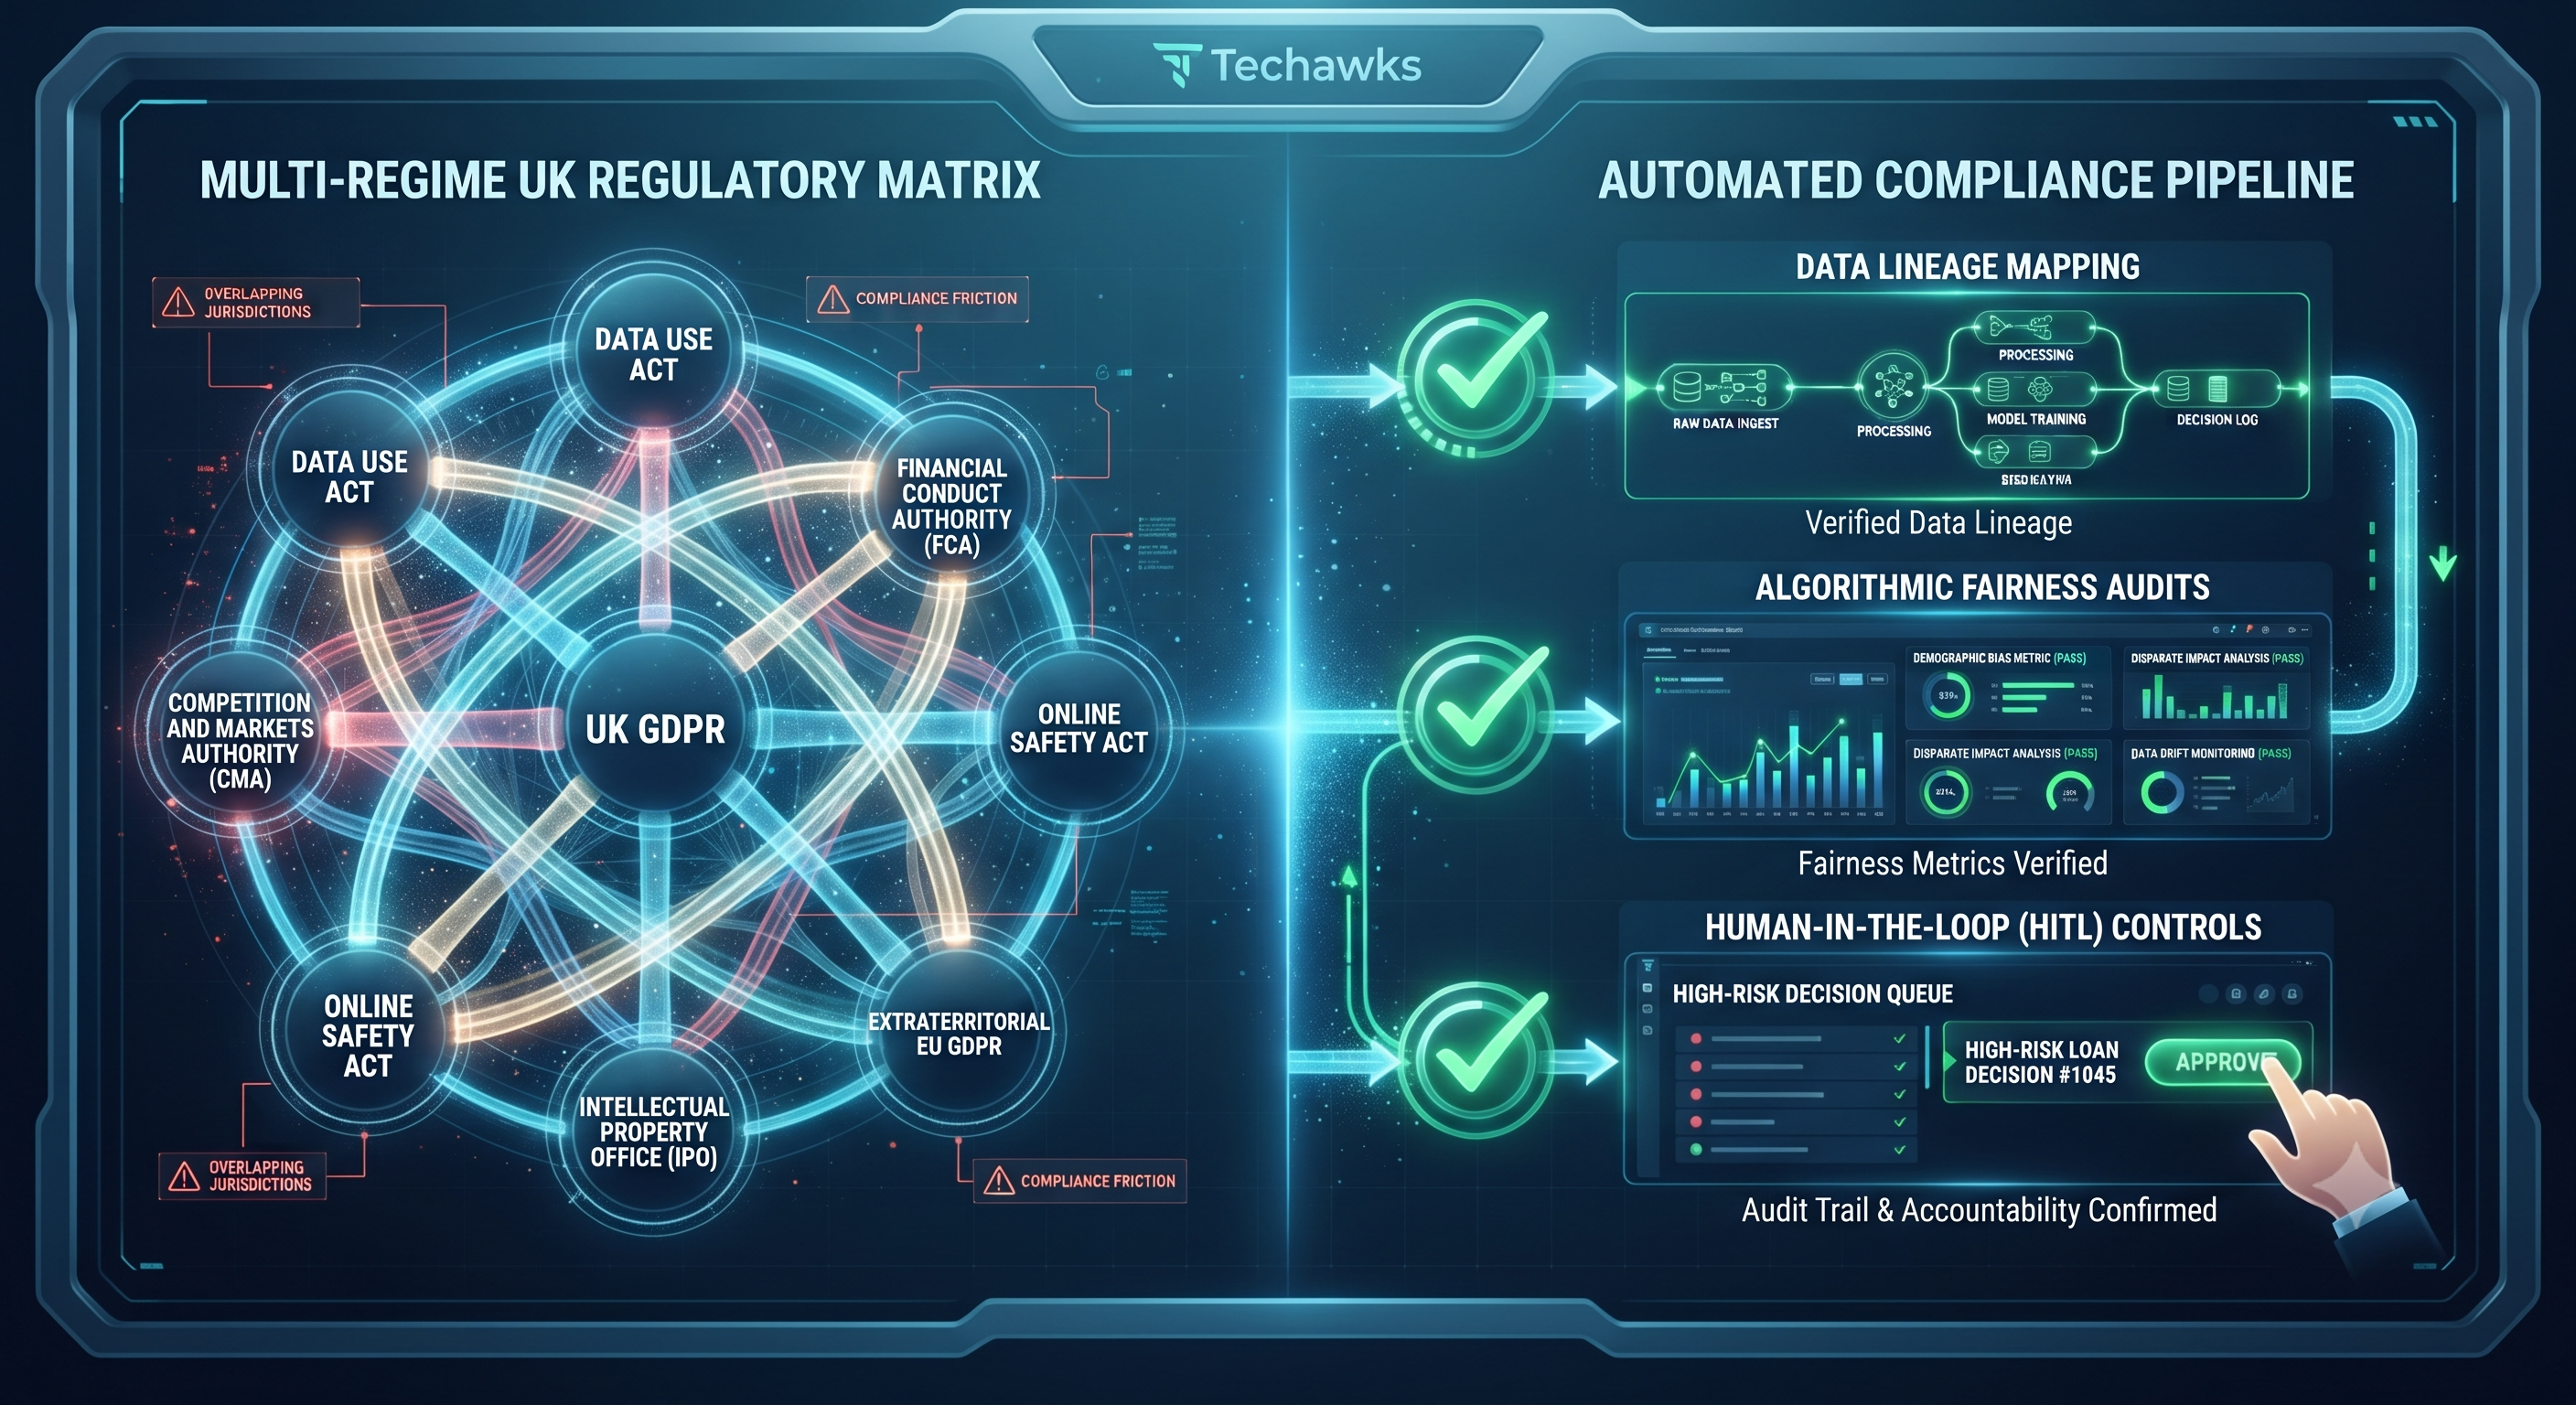
Step 1: Map Your Data Lineage and Processing Bases. Document every data input flowing into your models. Ensure automated decisions have clear justifications under UK data protection rules, with explicit audit trails for special category or personal data.
Step 2: Build Automated Algorithmic Fairness Audits. Integrate continuous evaluation tools into your CI/CD pipelines to monitor for demographic bias, disparate impact, and data drift before models hit production.
Step 3: Assign Named Accountability and HITL Controls. Implement strict human-in-the-loop (HITL) checkpoints for high-risk decisions and assign clear internal ownership to satisfy senior management accountability standards.
Discussion Question
How is your team handling multi-framework compliance without sacrificing deployment velocity? Let’s share regulatory strategies below! 👇
CTA (Join Techawks UK)
Ready to connect with top UK tech leaders, engineers, and compliance experts navigating the modern digital landscape? Join Techawks UK today to share architecture playbooks, collaborate locally, and lead the future of technology!
As British organizations rapidly adopt agentic AI and automated decision systems, compliance has shifted from a legal checklist into a core engineering requirement. Operating in the UK tech market means navigating multiple parallel regimes—including UK GDPR, data use standards, sector-specific oversight, and the extraterritorial reach of EU rules for teams serving cross-border users.
When autonomous agents process personal data or influence financial, medical, or operational decisions, static policy documents are no longer enough. Regulators expect transparent, auditable, and resilient system behavior.
Why This Matters
If your AI governance strategy relies entirely on reactive reviews, you risk regulatory friction, operational downtime, and severe reputational damage. Building a proactive compliance framework ensures your engineering pipelines can scale safely while maintaining clear accountability across your technical stack.
Mini-Tutorial: Implementing an Engineering-Led Compliance Harness
Protect your UK-based deployments and streamline regulatory readiness by embedding these three technical controls:
Step 1: Map Your Data Lineage and Processing Bases. Document every data input flowing into your models. Ensure automated decisions have clear justifications under UK data protection rules, with explicit audit trails for special category or personal data.
Step 2: Build Automated Algorithmic Fairness Audits. Integrate continuous evaluation tools into your CI/CD pipelines to monitor for demographic bias, disparate impact, and data drift before models hit production.
Step 3: Assign Named Accountability and HITL Controls. Implement strict human-in-the-loop (HITL) checkpoints for high-risk decisions and assign clear internal ownership to satisfy senior management accountability standards.
Discussion Question
How is your team handling multi-framework compliance without sacrificing deployment velocity? Let’s share regulatory strategies below! 👇
CTA (Join Techawks UK)
Ready to connect with top UK tech leaders, engineers, and compliance experts navigating the modern digital landscape? Join Techawks UK today to share architecture playbooks, collaborate locally, and lead the future of technology!
Navigating the Multi-Regime Maze: Building an AI Compliance Framework for UK Enterprises
As British organizations rapidly adopt agentic AI and automated decision systems, compliance has shifted from a legal checklist into a core engineering requirement. Operating in the UK tech market means navigating multiple parallel regimes—including UK GDPR, data use standards, sector-specific oversight, and the extraterritorial reach of EU rules for teams serving cross-border users.
When autonomous agents process personal data or influence financial, medical, or operational decisions, static policy documents are no longer enough. Regulators expect transparent, auditable, and resilient system behavior.
Why This Matters
If your AI governance strategy relies entirely on reactive reviews, you risk regulatory friction, operational downtime, and severe reputational damage. Building a proactive compliance framework ensures your engineering pipelines can scale safely while maintaining clear accountability across your technical stack.
Mini-Tutorial: Implementing an Engineering-Led Compliance Harness
Protect your UK-based deployments and streamline regulatory readiness by embedding these three technical controls:
Step 1: Map Your Data Lineage and Processing Bases. Document every data input flowing into your models. Ensure automated decisions have clear justifications under UK data protection rules, with explicit audit trails for special category or personal data.
Step 2: Build Automated Algorithmic Fairness Audits. Integrate continuous evaluation tools into your CI/CD pipelines to monitor for demographic bias, disparate impact, and data drift before models hit production.
Step 3: Assign Named Accountability and HITL Controls. Implement strict human-in-the-loop (HITL) checkpoints for high-risk decisions and assign clear internal ownership to satisfy senior management accountability standards.
Discussion Question
How is your team handling multi-framework compliance without sacrificing deployment velocity? Let’s share regulatory strategies below! 👇
CTA (Join Techawks UK)
Ready to connect with top UK tech leaders, engineers, and compliance experts navigating the modern digital landscape? Join Techawks UK today to share architecture playbooks, collaborate locally, and lead the future of technology!

 English
 Arabic
 French
 Spanish
 Portuguese
 Deutsch
 Turkish
 Dutch
 Italiano
 Russian
 Romaian
 Greek