Navigating UK AI Governance: The 4-Innovations Compliance Checklist for Enterprise Workflows
Unlike regions with a single centralized statute, the UK relies on a principles-based, sector-led approach governed via the UK GDPR, data protection reforms, and oversight from bodies like the ICO and sector regulators. When scaling AI systems that process personal data or automate consequential business decisions, structured compliance and rigorous data hygiene are critical to maintaining trust and operational continuity.
Use this practical 4-step checklist to ensure your AI systems align with modern UK enterprise standards:
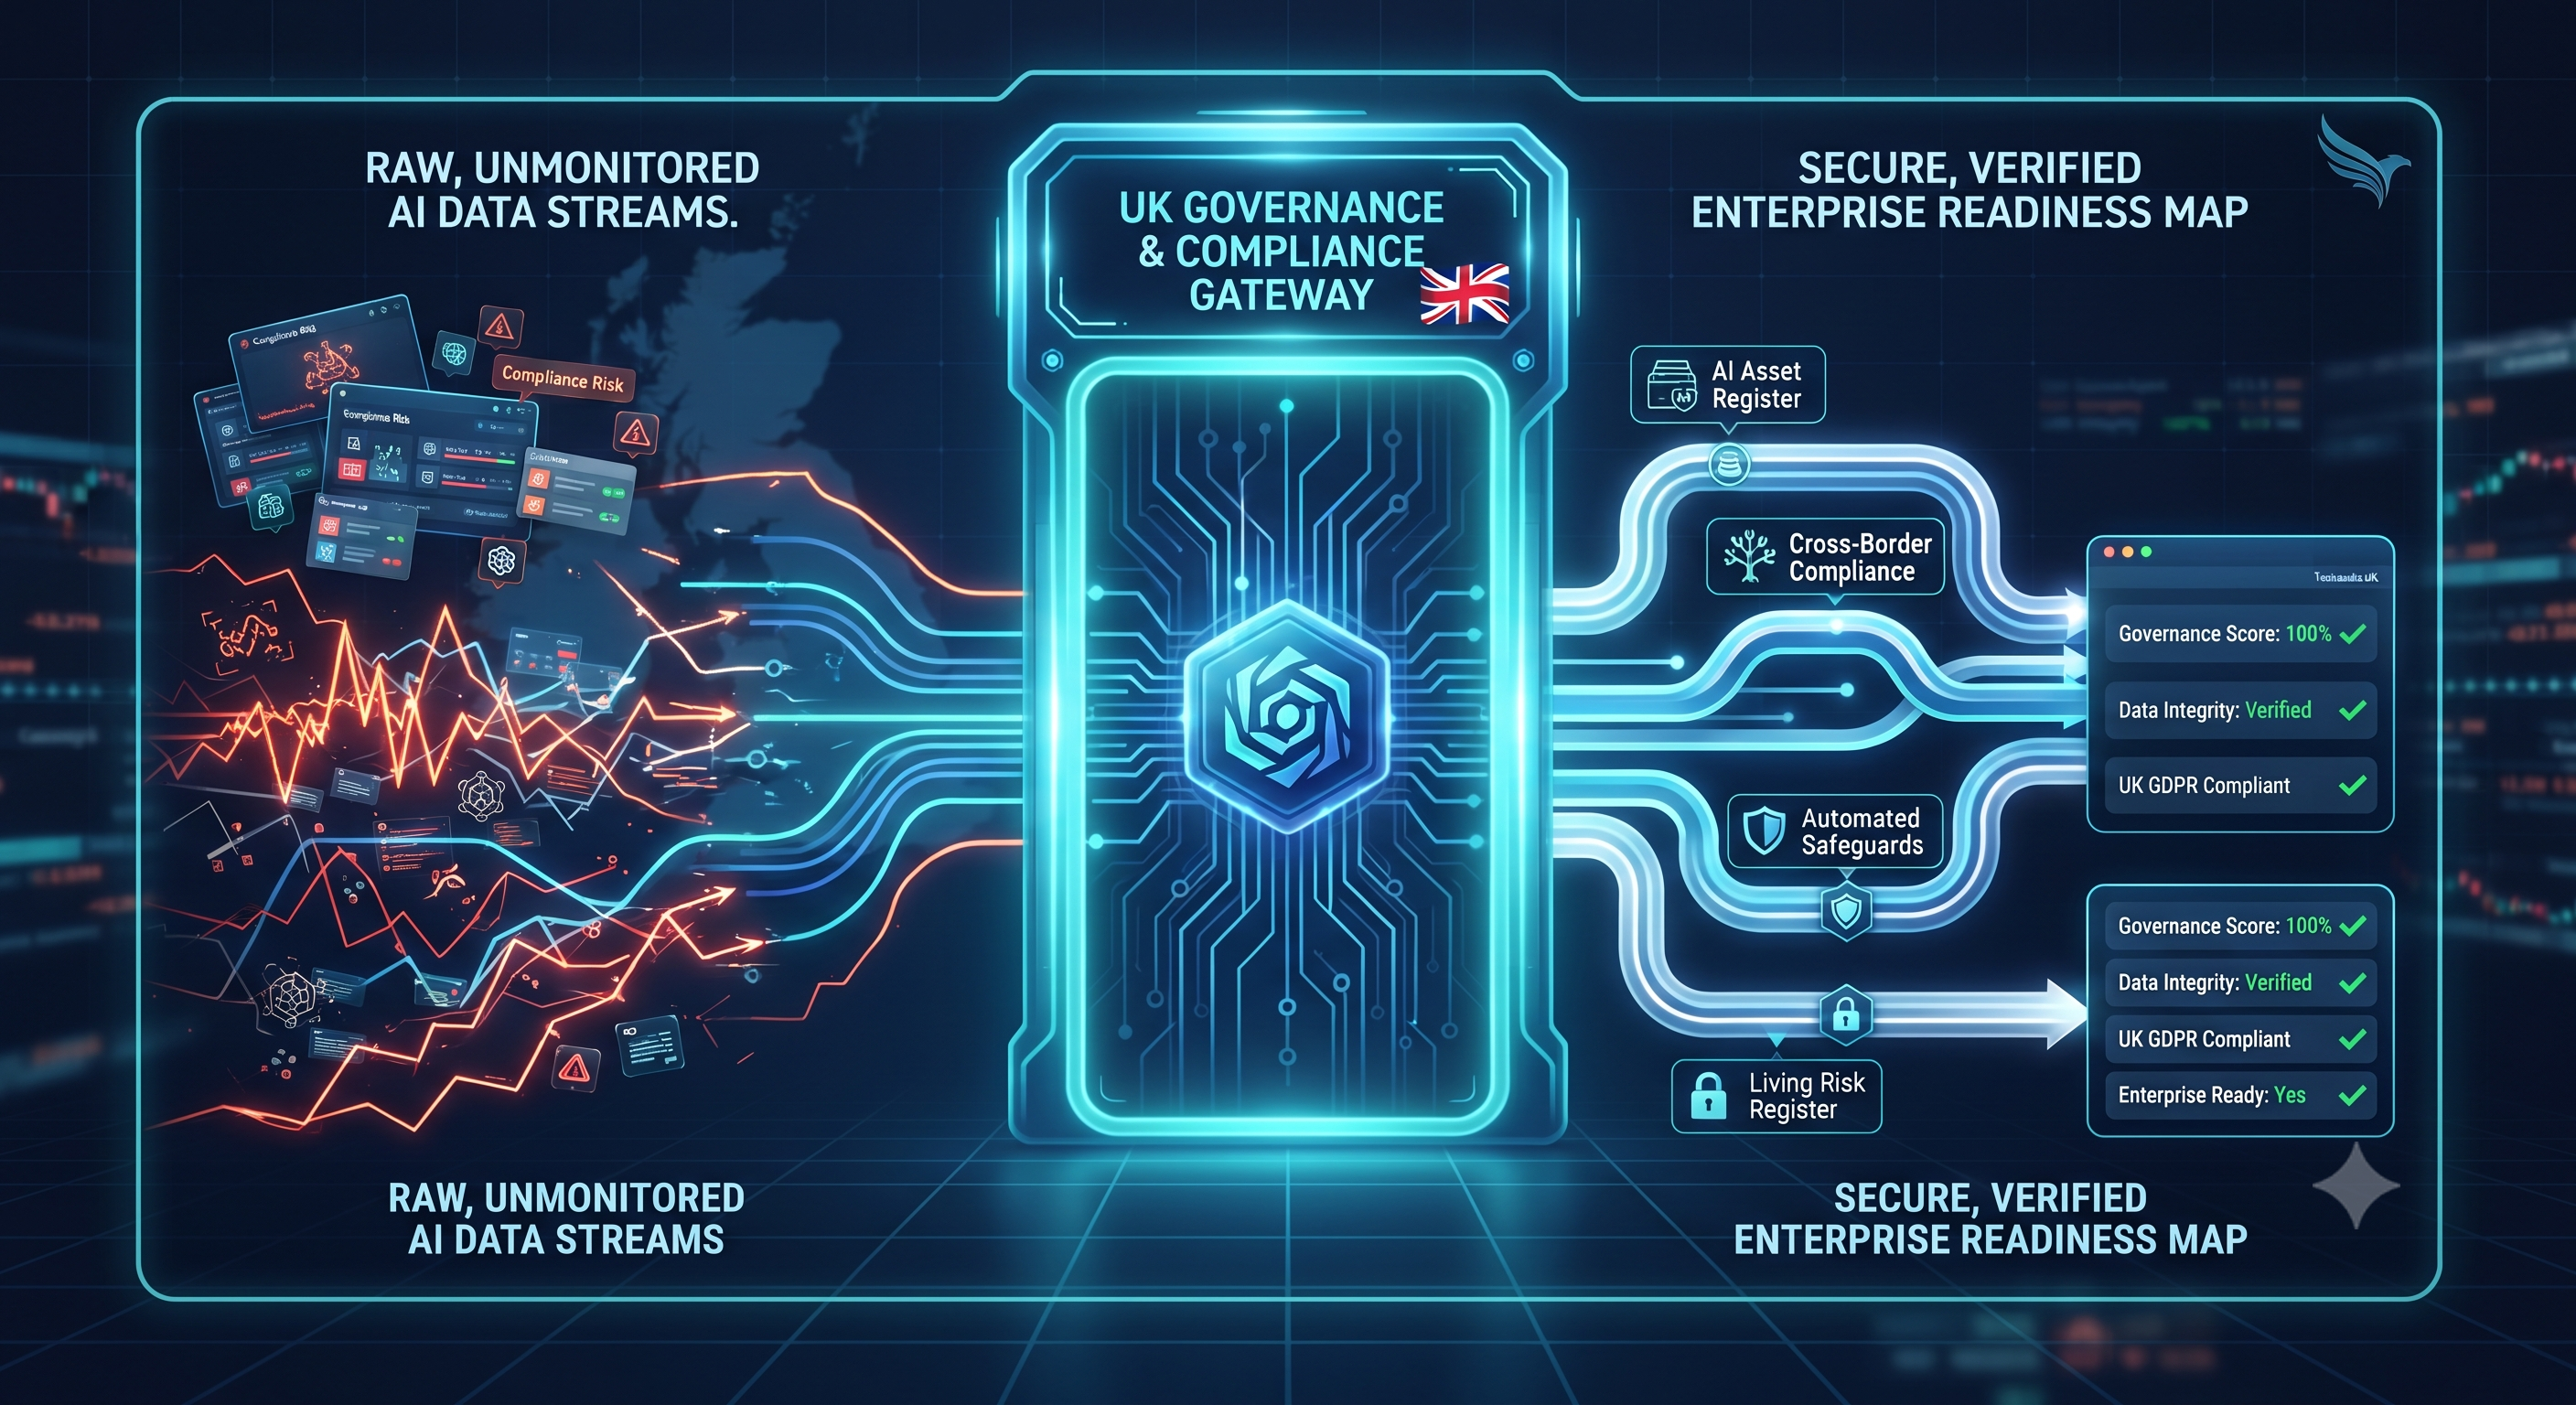
1. Build a Comprehensive AI Asset Register: Catalog every active machine learning model and embedded third-party AI tool across your tech stack so your board maintains absolute visibility over operational scope.
2. Map Cross-Border & Regulatory Exposure: Identify whether your systems trigger specific compliance obligations, such as the ICO’s data protection codes or extraterritorial reach from international frameworks.
3. Implement Robust Automated Decision Safeguards: Ensure transparency, meaningful human review options, and strict lawful bases are documented when AI materially influences decisions affecting individuals.
4. Establish Living Risk & Governance Registers: Move away from static box-ticking audits by assigning clear executive accountability and continuous monitoring protocols for model drift and bias.
Discussion Question
How is your engineering or compliance team handling the multi-framework regulatory environment across the UK tech sector? Let’s share your strategies below!
CTA (Join Techawks UK)
Ready to build resilient systems, stay ahead of regulatory shifts, and connect with top technology professionals across the country? Join the Techawks UK community today to collaborate and elevate your engineering career.
Navigating UK AI Governance: The 4-Innovations Compliance Checklist for Enterprise Workflows
Unlike regions with a single centralized statute, the UK relies on a principles-based, sector-led approach governed via the UK GDPR, data protection reforms, and oversight from bodies like the ICO and sector regulators. When scaling AI systems that process personal data or automate consequential business decisions, structured compliance and rigorous data hygiene are critical to maintaining trust and operational continuity.
Use this practical 4-step checklist to ensure your AI systems align with modern UK enterprise standards:
1. Build a Comprehensive AI Asset Register: Catalog every active machine learning model and embedded third-party AI tool across your tech stack so your board maintains absolute visibility over operational scope.
2. Map Cross-Border & Regulatory Exposure: Identify whether your systems trigger specific compliance obligations, such as the ICO’s data protection codes or extraterritorial reach from international frameworks.
3. Implement Robust Automated Decision Safeguards: Ensure transparency, meaningful human review options, and strict lawful bases are documented when AI materially influences decisions affecting individuals.
4. Establish Living Risk & Governance Registers: Move away from static box-ticking audits by assigning clear executive accountability and continuous monitoring protocols for model drift and bias.
Discussion Question
How is your engineering or compliance team handling the multi-framework regulatory environment across the UK tech sector? Let’s share your strategies below!
CTA (Join Techawks UK)
Ready to build resilient systems, stay ahead of regulatory shifts, and connect with top technology professionals across the country? Join the Techawks UK community today to collaborate and elevate your engineering career.

 English
 French
 Spanish
 Portuguese
 Deutsch
 Turkish
 Dutch
 Italiano
 Russian
 Romaian
 Portuguese (Brazil)
 Greek