Navigating the Enterprise AI Shift: Why SOC 2 Compliance and Data Governance Are Make-or-Break for US Tech Startups
As engineering and product leaders building for the US tech landscape, compliance is often viewed as a painful hurdle pushed off until Series A. But with enterprise buyers demanding strict data isolation and zero-retention guarantees from third-party AI tools, security posture is your biggest competitive differentiator.
Enter Automated Compliance and Trust Infrastructure:
Passing a security audit doesn’t mean drowning in spreadsheets. Modern engineering teams are standardizing on continuous compliance and data governance frameworks:
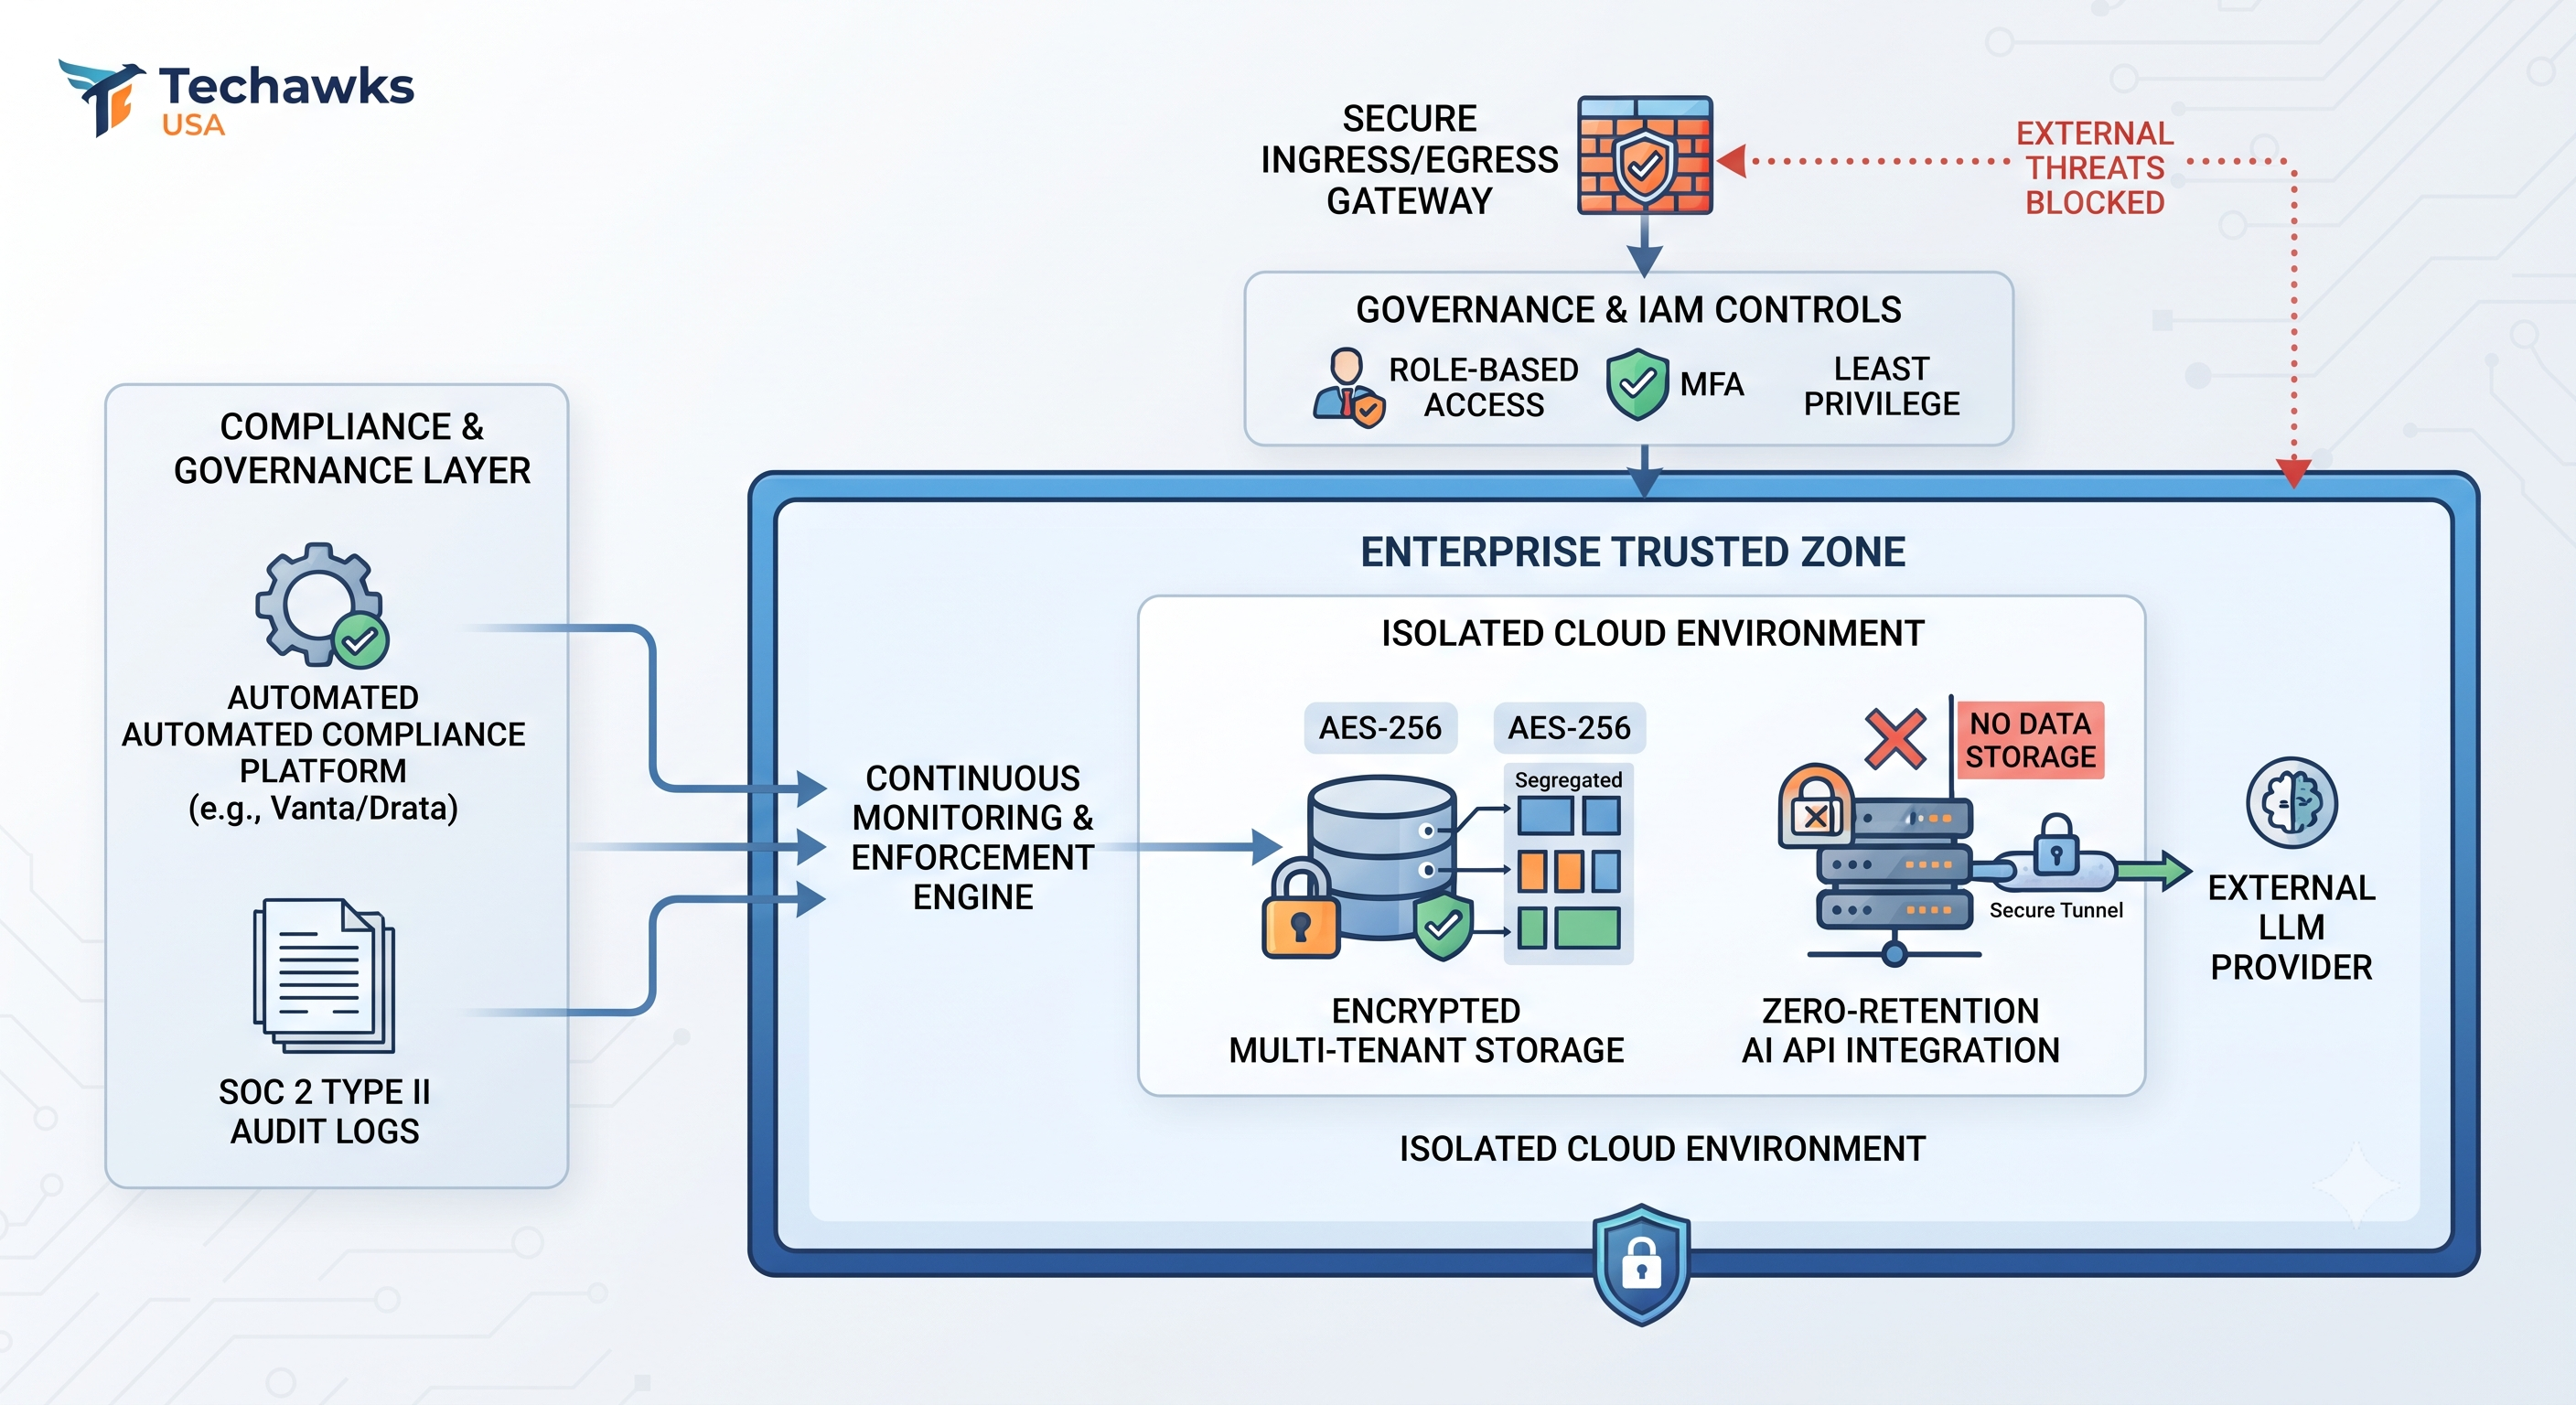
Automate Infrastructure Monitoring: Use continuous compliance tools (like Vanta or Drata) integrated directly into your AWS/GCP and GitHub workflows to monitor access controls, encryption standards, and IAM policies automatically.
Enforce Strict Data Boundaries: When integrating LLMs or processing enterprise payloads, ensure multi-tenant data isolation and implement zero-data-retention policies with API providers to satisfy corporate legal teams.
Maintain Immutable Audit Logs: Keep centralized, tamper-proof audit trails of all production deployments, privilege escalations, and database queries to accelerate enterprise security reviews.
By baking governance and automated compliance directly into your development lifecycle, you turn enterprise security from a blocker into your fastest path to closing six-figure deals.
Discussion Question: Have you ever had an enterprise deal delayed over SOC 2 or data privacy requirements, and how did your engineering team adapt? Let’s talk strategy below! 👇
CTA (Join Techawks USA): Ready to scale your tech career, startup, or engineering systems in the US market? Join our community of professionals and builders at Techawks USA to master the playbooks that matter.
Navigating the Enterprise AI Shift: Why SOC 2 Compliance and Data Governance Are Make-or-Break for US Tech Startups
As engineering and product leaders building for the US tech landscape, compliance is often viewed as a painful hurdle pushed off until Series A. But with enterprise buyers demanding strict data isolation and zero-retention guarantees from third-party AI tools, security posture is your biggest competitive differentiator.
Enter Automated Compliance and Trust Infrastructure:
Passing a security audit doesn’t mean drowning in spreadsheets. Modern engineering teams are standardizing on continuous compliance and data governance frameworks:
Automate Infrastructure Monitoring: Use continuous compliance tools (like Vanta or Drata) integrated directly into your AWS/GCP and GitHub workflows to monitor access controls, encryption standards, and IAM policies automatically.
Enforce Strict Data Boundaries: When integrating LLMs or processing enterprise payloads, ensure multi-tenant data isolation and implement zero-data-retention policies with API providers to satisfy corporate legal teams.
Maintain Immutable Audit Logs: Keep centralized, tamper-proof audit trails of all production deployments, privilege escalations, and database queries to accelerate enterprise security reviews.
By baking governance and automated compliance directly into your development lifecycle, you turn enterprise security from a blocker into your fastest path to closing six-figure deals.
Discussion Question: Have you ever had an enterprise deal delayed over SOC 2 or data privacy requirements, and how did your engineering team adapt? Let’s talk strategy below! 👇
CTA (Join Techawks USA): Ready to scale your tech career, startup, or engineering systems in the US market? Join our community of professionals and builders at Techawks USA to master the playbooks that matter.

 English
 Arabic
 French
 Spanish
 Deutsch
 Turkish
 Dutch
 Italiano
 Russian
 Romaian
 Portuguese (Brazil)
 Greek