Navigating the UAE AI Act & PDPL: Why Sovereign Data Architecture and Privacy-First AI Are Essential for Regional Tech
As the UAE leads the region in the digital economy, tech builders and enterprise architects face a crucial reality: treating artificial intelligence and data management as an afterthought is no longer viable. Under current regulatory frameworks, processing sensitive resident data or utilizing third-party AI models requires transparent, localized control.
Enter Sovereign AI Gateways and Privacy-First Compliance Tooling:
To harness the power of artificial intelligence while staying fully compliant with regional data mandates, modern engineering teams are shifting toward sovereign architecture patterns:
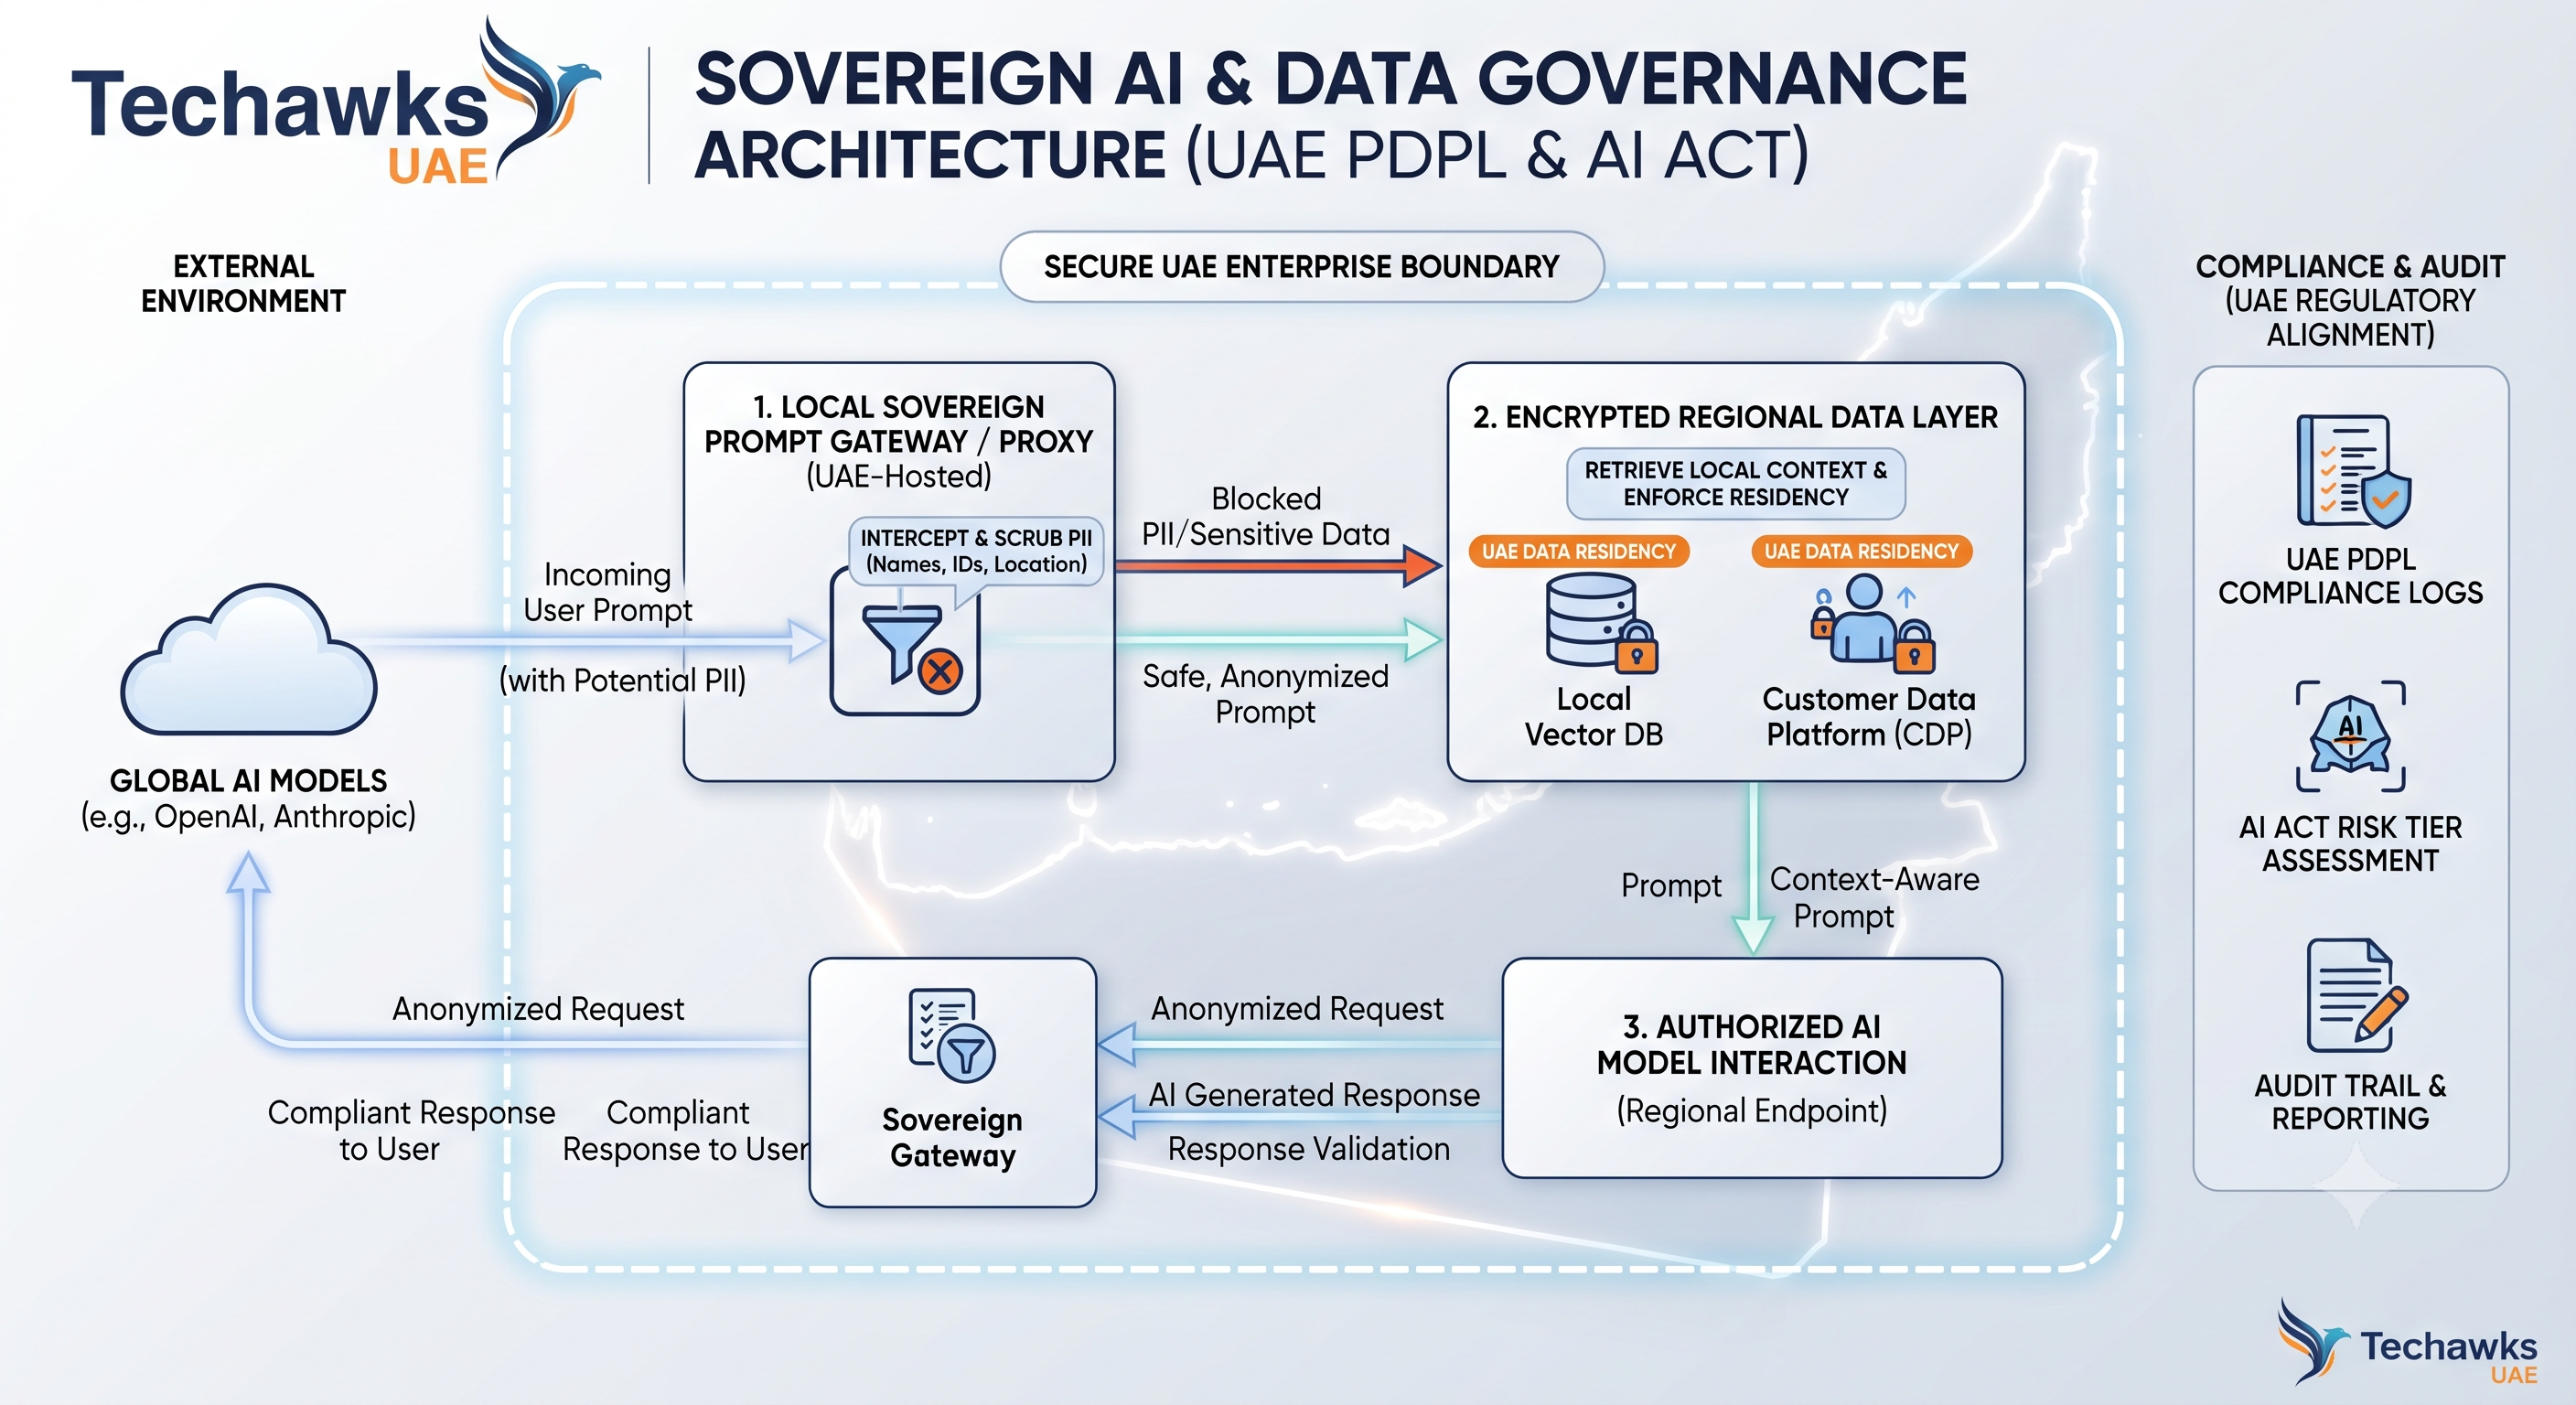
Implement Prompt Interception & Data Masking: Use gateway tools (such as localized proxy wrappers) to scrub Personally Identifiable Information (PII), credentials, and proprietary business logic before payloads hit external third-party LLM endpoints.
Enforce Local Data Residency: Ensure your vector databases, customer records, and training artifacts reside within regional cloud zones (such as UAE-based data centers) to satisfy local data localization expectations.
Automate Risk Tier Self-Assessments: Systematically inventory every AI component, automation script, and embedded ML utility in your stack to map them against designated transparency and risk tiers.
By designing your systems with built-in data sovereignty and compliance guardrails from day one, you protect user privacy, mitigate legal risk, and accelerate enterprise adoption across the Emirates.
Discussion Question: How is your team handling data residency and compliance requirements when integrating AI models into your UAE applications? Let’s share your architecture strategies below! 👇
CTA (Join Techawks UAE): Ready to build world-class, compliant technology systems for the fast-growing UAE market? Join our community of developers, engineers, and innovators at Techawks UAE to master the tools that matter.
Navigating the UAE AI Act & PDPL: Why Sovereign Data Architecture and Privacy-First AI Are Essential for Regional Tech
As the UAE leads the region in the digital economy, tech builders and enterprise architects face a crucial reality: treating artificial intelligence and data management as an afterthought is no longer viable. Under current regulatory frameworks, processing sensitive resident data or utilizing third-party AI models requires transparent, localized control.
Enter Sovereign AI Gateways and Privacy-First Compliance Tooling:
To harness the power of artificial intelligence while staying fully compliant with regional data mandates, modern engineering teams are shifting toward sovereign architecture patterns:
Implement Prompt Interception & Data Masking: Use gateway tools (such as localized proxy wrappers) to scrub Personally Identifiable Information (PII), credentials, and proprietary business logic before payloads hit external third-party LLM endpoints.
Enforce Local Data Residency: Ensure your vector databases, customer records, and training artifacts reside within regional cloud zones (such as UAE-based data centers) to satisfy local data localization expectations.
Automate Risk Tier Self-Assessments: Systematically inventory every AI component, automation script, and embedded ML utility in your stack to map them against designated transparency and risk tiers.
By designing your systems with built-in data sovereignty and compliance guardrails from day one, you protect user privacy, mitigate legal risk, and accelerate enterprise adoption across the Emirates.
Discussion Question: How is your team handling data residency and compliance requirements when integrating AI models into your UAE applications? Let’s share your architecture strategies below! 👇
CTA (Join Techawks UAE): Ready to build world-class, compliant technology systems for the fast-growing UAE market? Join our community of developers, engineers, and innovators at Techawks UAE to master the tools that matter.

 English
 Arabic
 French
 Spanish
 Portuguese
 Deutsch
 Turkish
 Italiano
 Russian
 Romaian
 Portuguese (Brazil)
 Greek