The US Tech Compliance & SOC 2 Readiness Checklist: 5 Core Trust Pillars for Scaling SaaS Startups
As US technology startups scale from early seed traction to enterprise-ready growth, establishing automated compliance and rigorous data governance is non-negotiable. Passing an audit isn't just about checking legal boxes; it’s about proving to customers that their data is protected by enterprise-grade guardrails from day one.
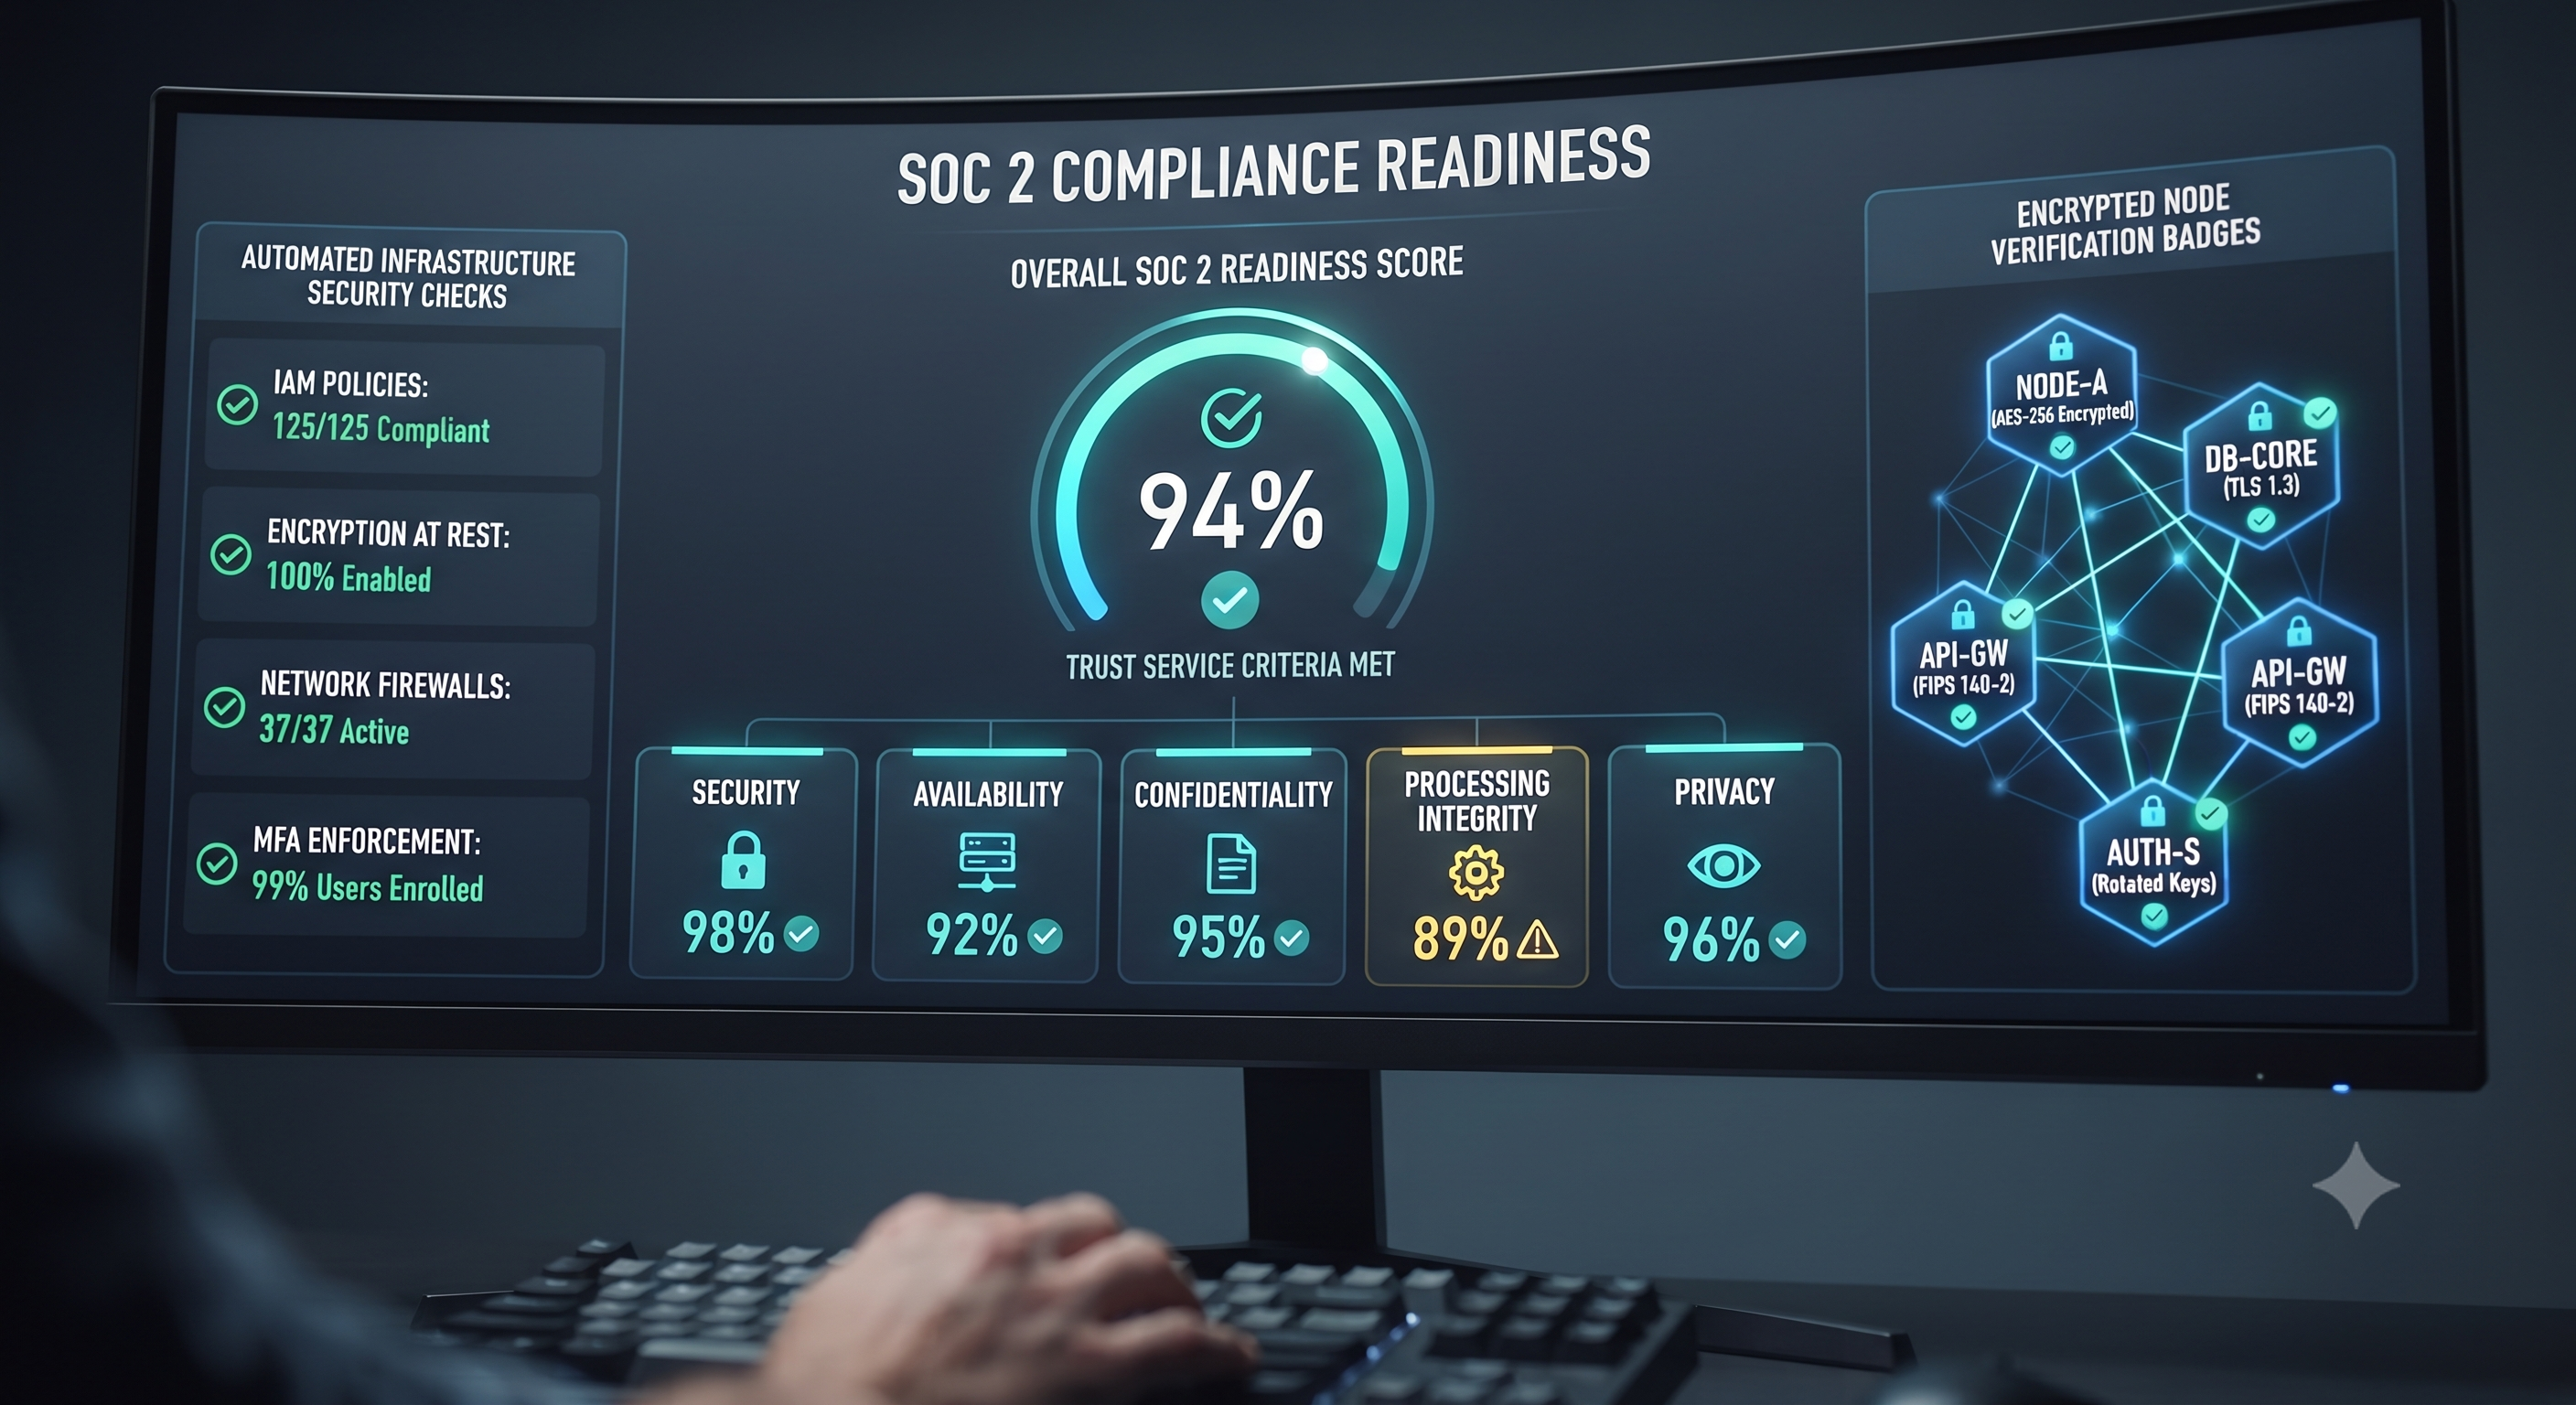
Audit and fortify your infrastructure for enterprise procurement with this SOC 2 readiness checklist:
[ ] Automated Identity & Access Management (IAM): Enforce strict multi-factor authentication (MFA), role-based access control (RBAC), and automated offboarding across all internal developer tools and cloud consoles.
[ ] Continuous Infrastructure Monitoring: Implement automated compliance scanners and log centralization tools to detect unauthorized configuration changes or security drift in real time.
[ ] Version-Controlled Access & Change Management: Ensure every production code deployment, database migration, and infrastructure update goes through mandatory pull request reviews and CI/CD audit trails.
[ ] Encrypted Data at Rest & in Transit: Mandate robust encryption standards (AES-256 for storage, TLS 1.3 for transit) backed by automated key rotation via AWS KMS or HashiCorp Vault.
[ ] Formalized Incident Response Playbook: Document, test, and automate your incident detection, escalation, and post-mortem workflows so you can respond transparently to enterprise security questionnaires.
Why It Matters
Enterprise buyers don't just buy software—they buy risk reduction. Building compliance into your engineering workflow early accelerates your sales cycle, builds instant market trust, and sets your startup apart in a crowded ecosystem.
Discussion Question
What has been your startup's biggest bottleneck when transitioning from an ad-hoc security setup to formal SOC 2 compliance for enterprise sales? Let’s share notes below! 👇
CTA (Join Techawks USA)
Ready to build, scale, and sell to US enterprises? Join the Techawks USA community to connect with local founders, share compliance strategies, and accelerate your growth.
The US Tech Compliance & SOC 2 Readiness Checklist: 5 Core Trust Pillars for Scaling SaaS Startups
As US technology startups scale from early seed traction to enterprise-ready growth, establishing automated compliance and rigorous data governance is non-negotiable. Passing an audit isn't just about checking legal boxes; it’s about proving to customers that their data is protected by enterprise-grade guardrails from day one.
Audit and fortify your infrastructure for enterprise procurement with this SOC 2 readiness checklist:
[ ] Automated Identity & Access Management (IAM): Enforce strict multi-factor authentication (MFA), role-based access control (RBAC), and automated offboarding across all internal developer tools and cloud consoles.
[ ] Continuous Infrastructure Monitoring: Implement automated compliance scanners and log centralization tools to detect unauthorized configuration changes or security drift in real time.
[ ] Version-Controlled Access & Change Management: Ensure every production code deployment, database migration, and infrastructure update goes through mandatory pull request reviews and CI/CD audit trails.
[ ] Encrypted Data at Rest & in Transit: Mandate robust encryption standards (AES-256 for storage, TLS 1.3 for transit) backed by automated key rotation via AWS KMS or HashiCorp Vault.
[ ] Formalized Incident Response Playbook: Document, test, and automate your incident detection, escalation, and post-mortem workflows so you can respond transparently to enterprise security questionnaires.
Why It Matters
Enterprise buyers don't just buy software—they buy risk reduction. Building compliance into your engineering workflow early accelerates your sales cycle, builds instant market trust, and sets your startup apart in a crowded ecosystem.
Discussion Question
What has been your startup's biggest bottleneck when transitioning from an ad-hoc security setup to formal SOC 2 compliance for enterprise sales? Let’s share notes below! 👇
CTA (Join Techawks USA)
Ready to build, scale, and sell to US enterprises? Join the Techawks USA community to connect with local founders, share compliance strategies, and accelerate your growth.

 Arabic
 French
 Spanish
 Portuguese
 Deutsch
 Turkish
 Dutch
 Italiano
 Russian
 Romaian
 Portuguese (Brazil)
 Greek