The Compliance Reality Check: Navigating the Multi-Regulator AI Landscape in the UK
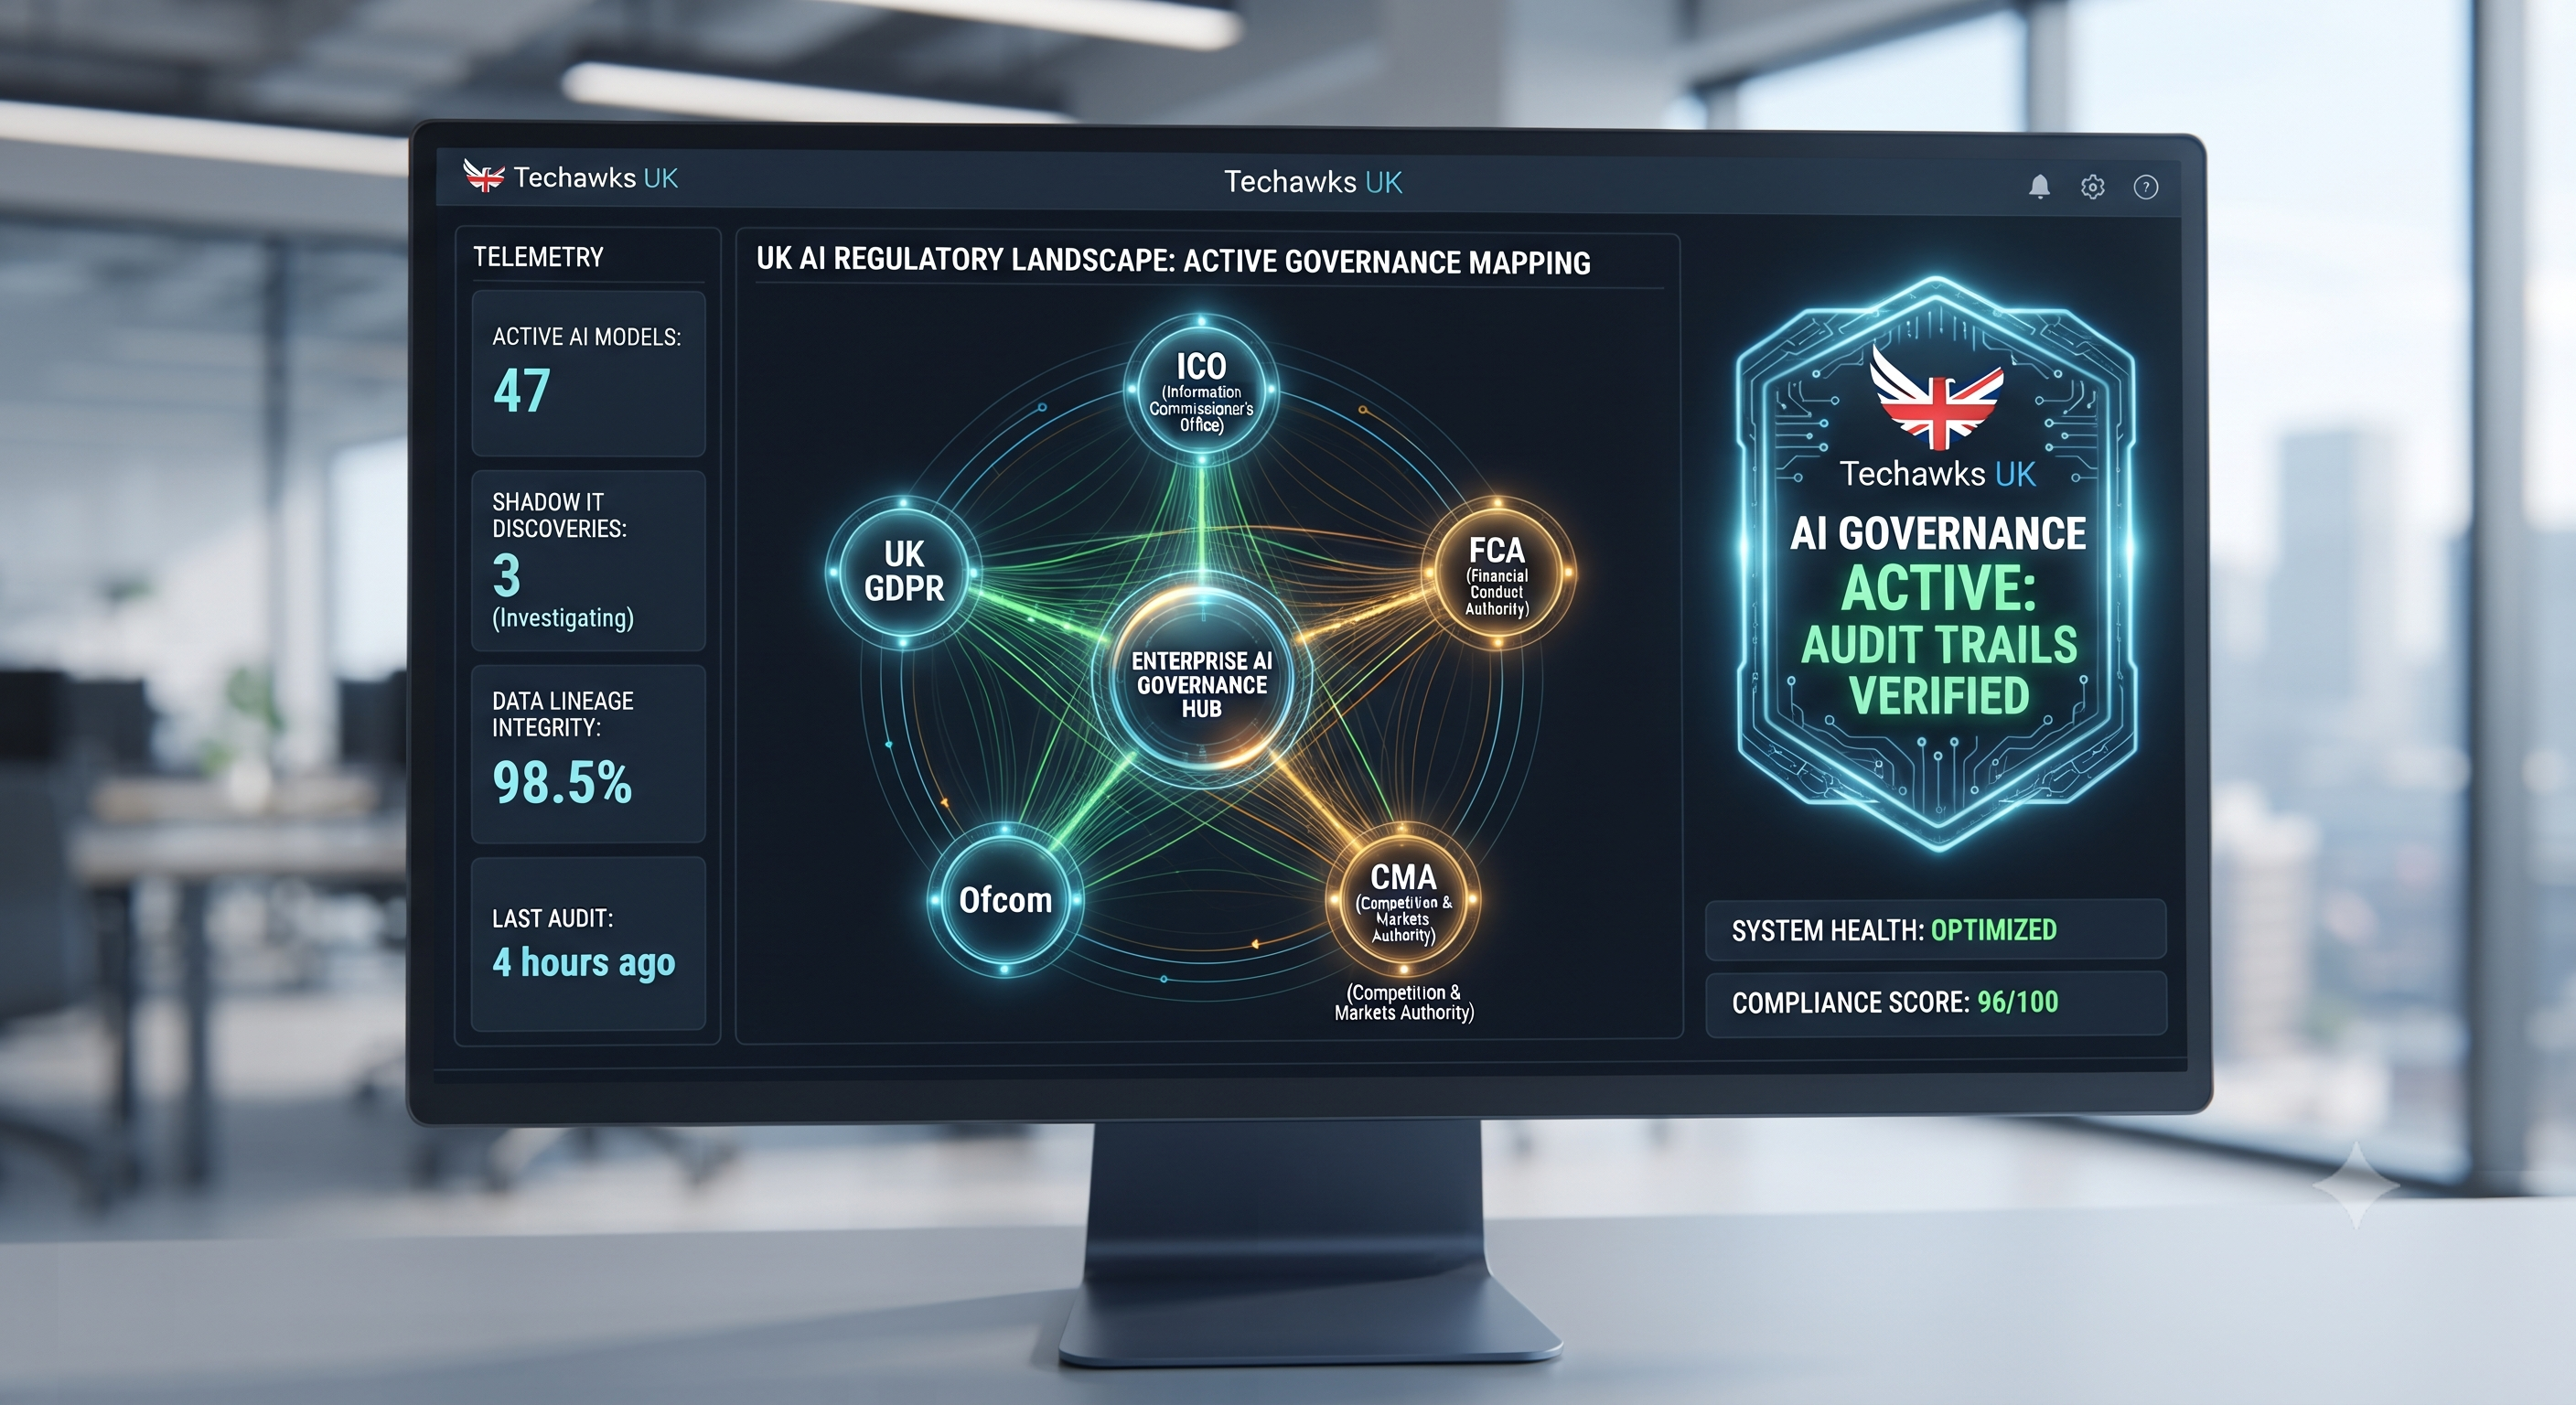
The United Kingdom technology sector operates on a distinct, sector-led approach to artificial intelligence and data governance. Rather than a unified legislative rulebook, oversight is distributed across key regulators—including the Information Commissioner’s Office (ICO), the Financial Conduct Authority (FCA), Ofcom, and the Competition and Markets Authority (CMA)—applying core principles of safety, transparency, fairness, and accountability.
Why It Matters
As UK enterprises rapidly shift from experimental AI pilots to deploying autonomous agents and production-grade models, regulatory scrutiny has intensified—especially concerning data protection, automated decision-making, and extraterritorial exposures like the EU AI Act. Organizations that fail to maintain active visibility, robust data hygiene, and clear documentation risk costly operational friction, loss of enterprise trust, and severe compliance gaps.
What You Need to Know (The UK Compliance Playbook)
To future-proof your tech stack and embed governance directly into your engineering workflows, focus on three essential steps:
Build a Living AI Risk Register: Move beyond static assessments. Maintain an active inventory of all algorithms, APIs, and shadow AI tools in use, assigning explicit ownership and regular review cycles to tech leads.
Operationalize Data Governance and Transparency: Ensure your data pipelines maintain strict hygiene standards, clear lineage, and documented Data Protection Impact Assessments (DPIAs) to meet ICO expectations for automated processing.
Align with Sector-Specific Standards: Map your technical controls across multiple frameworks simultaneously—incorporating UK GDPR requirements, sector rules, and international benchmarks like ISO/IEC 42001 to prove resilience and security.
Discussion Question
How is your engineering or product team handling compliance and multi-regulator oversight in the UK? Are you finding it challenging to balance rapid deployment with governance? Let's discuss below! 👇
CTA (Join Techawks UK)
Want to connect with UK technologists, developers, and leaders navigating the forefront of AI, cloud, and tech compliance? Join Techawks UK today to share strategies and elevate your engineering journey!
The Compliance Reality Check: Navigating the Multi-Regulator AI Landscape in the UK
The United Kingdom technology sector operates on a distinct, sector-led approach to artificial intelligence and data governance. Rather than a unified legislative rulebook, oversight is distributed across key regulators—including the Information Commissioner’s Office (ICO), the Financial Conduct Authority (FCA), Ofcom, and the Competition and Markets Authority (CMA)—applying core principles of safety, transparency, fairness, and accountability.
Why It Matters
As UK enterprises rapidly shift from experimental AI pilots to deploying autonomous agents and production-grade models, regulatory scrutiny has intensified—especially concerning data protection, automated decision-making, and extraterritorial exposures like the EU AI Act. Organizations that fail to maintain active visibility, robust data hygiene, and clear documentation risk costly operational friction, loss of enterprise trust, and severe compliance gaps.
What You Need to Know (The UK Compliance Playbook)
To future-proof your tech stack and embed governance directly into your engineering workflows, focus on three essential steps:
Build a Living AI Risk Register: Move beyond static assessments. Maintain an active inventory of all algorithms, APIs, and shadow AI tools in use, assigning explicit ownership and regular review cycles to tech leads.
Operationalize Data Governance and Transparency: Ensure your data pipelines maintain strict hygiene standards, clear lineage, and documented Data Protection Impact Assessments (DPIAs) to meet ICO expectations for automated processing.
Align with Sector-Specific Standards: Map your technical controls across multiple frameworks simultaneously—incorporating UK GDPR requirements, sector rules, and international benchmarks like ISO/IEC 42001 to prove resilience and security.
Discussion Question
How is your engineering or product team handling compliance and multi-regulator oversight in the UK? Are you finding it challenging to balance rapid deployment with governance? Let's discuss below! 👇
CTA (Join Techawks UK)
Want to connect with UK technologists, developers, and leaders navigating the forefront of AI, cloud, and tech compliance? Join Techawks UK today to share strategies and elevate your engineering journey!

 English
 Arabic
 French
 Spanish
 Portuguese
 Deutsch
 Turkish
 Dutch
 Russian
 Romaian
 Portuguese (Brazil)
 Greek