Myth vs. Fact: Is Your Cloud Stack Compliant with the UAE Personal Data Protection Law (PDPL)?
❌ Myth 1: "If our cloud database resides in the UAE, we fully satisfy data sovereignty requirements."
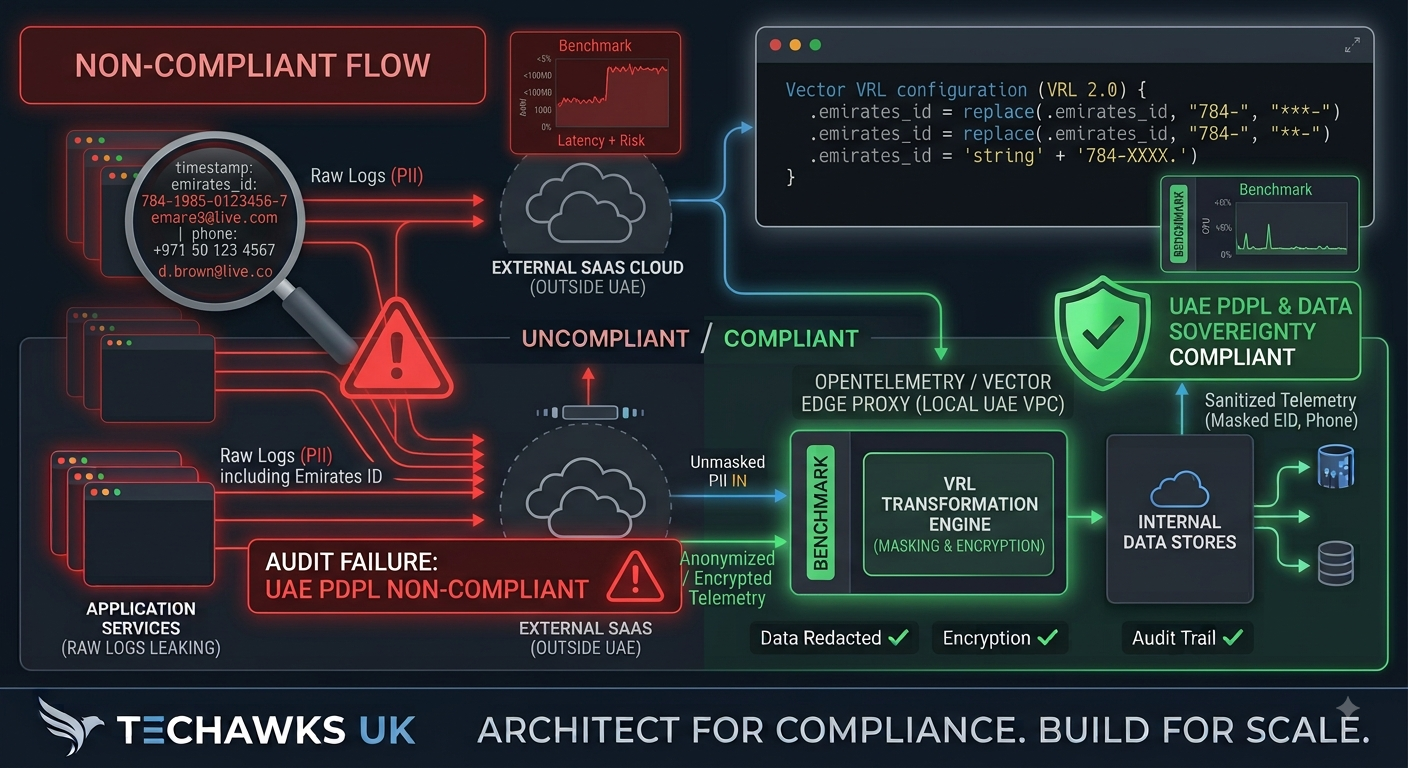
Fact: Storing data in-region is only half of the equation. Under UAE PDPL, data flow matters just as much as data rest. If application traces, telemetry metrics, or operational debug logs stream unmasked personal data—such as Emirates IDs (784-XXXX...), personal emails, or contact numbers—to third-party SaaS vendors hosted outside the GCC without edge sanitization, you are conducting unauthorized cross-border data transfers.
❌ Myth 2: "Log entries and system diagnostics don't count as personal data."
Fact: The UAE PDPL defines personal data broadly as any information that can directly or indirectly identify an individual. System logs containing IP addresses, device identifiers, or user transaction metadata fall squarely under regulatory scrutiny. Leaving debug logs unredacted in long-term storage or forwarding them unmasked to global monitoring dashboards creates a major compliance gap.
🛠️ Actionable Advice: How to Architect a PDPL-Compliant Pipeline
Scrub at the VPC Perimeter: Deploy local ingestion proxies (such as an OpenTelemetry Collector or Vector node) directly inside your UAE cloud VPC.
Automate Ingestion-Layer Masking: Apply transformation rules at the proxy layer to automatically redact Emirates IDs, scrub mobile numbers, and hash user handles before data leaves the VPC boundary.
Enforce Dual-Stream Routing: Send fully anonymized, sanitized telemetry to external SaaS monitoring platforms while retaining raw, encrypted, access-controlled audit logs inside secure local storage.
Key Takeaways
Data Flow Matters: In-region hosting does not protect you if outbound telemetry streams export raw personal data across borders.
Logs Are In-Scope: Under UAE PDPL, online identifiers and log entries count as personal data.
Redact at the Ingestion Layer: Use edge collectors (OpenTelemetry/Vector) within your UAE VPC to scrub PII prior to egress.
CTA (Join Techawks UAE)
Looking to align your cloud infrastructure with GCC data governance standards?
👉 [Join Techawks UAE today] to connect with local system architects, access compliant cloud blueprints, and build scalable systems built for the Middle East tech ecosystem.
Myth vs. Fact: Is Your Cloud Stack Compliant with the UAE Personal Data Protection Law (PDPL)?
❌ Myth 1: "If our cloud database resides in the UAE, we fully satisfy data sovereignty requirements."
Fact: Storing data in-region is only half of the equation. Under UAE PDPL, data flow matters just as much as data rest. If application traces, telemetry metrics, or operational debug logs stream unmasked personal data—such as Emirates IDs (784-XXXX...), personal emails, or contact numbers—to third-party SaaS vendors hosted outside the GCC without edge sanitization, you are conducting unauthorized cross-border data transfers.
❌ Myth 2: "Log entries and system diagnostics don't count as personal data."
Fact: The UAE PDPL defines personal data broadly as any information that can directly or indirectly identify an individual. System logs containing IP addresses, device identifiers, or user transaction metadata fall squarely under regulatory scrutiny. Leaving debug logs unredacted in long-term storage or forwarding them unmasked to global monitoring dashboards creates a major compliance gap.
🛠️ Actionable Advice: How to Architect a PDPL-Compliant Pipeline
Scrub at the VPC Perimeter: Deploy local ingestion proxies (such as an OpenTelemetry Collector or Vector node) directly inside your UAE cloud VPC.
Automate Ingestion-Layer Masking: Apply transformation rules at the proxy layer to automatically redact Emirates IDs, scrub mobile numbers, and hash user handles before data leaves the VPC boundary.
Enforce Dual-Stream Routing: Send fully anonymized, sanitized telemetry to external SaaS monitoring platforms while retaining raw, encrypted, access-controlled audit logs inside secure local storage.
Key Takeaways
Data Flow Matters: In-region hosting does not protect you if outbound telemetry streams export raw personal data across borders.
Logs Are In-Scope: Under UAE PDPL, online identifiers and log entries count as personal data.
Redact at the Ingestion Layer: Use edge collectors (OpenTelemetry/Vector) within your UAE VPC to scrub PII prior to egress.
CTA (Join Techawks UAE)
Looking to align your cloud infrastructure with GCC data governance standards?
👉 [Join Techawks UAE today] to connect with local system architects, access compliant cloud blueprints, and build scalable systems built for the Middle East tech ecosystem.

 English
 Arabic
 French
 Spanish
 Portuguese
 Deutsch
 Turkish
 Dutch
 Italiano
 Romaian
 Portuguese (Brazil)
 Greek